CVE-2024-31570 - Breaking Down the Buffer Overflow in FreeImage’s XPM Loader (With Exploit Snippet)
CVE-2024-31570 is a critical stack-based buffer overflow vulnerability that affects the libfreeimage library, a very popular image processing toolkit used in many
CVE-2024-38016 - Microsoft Office Visio Remote Code Execution Vulnerability Explained
---
Microsoft Office Visio, a tool many companies use to make diagrams and flowcharts, recently faced a serious security problem. This post breaks down CVE-2024-
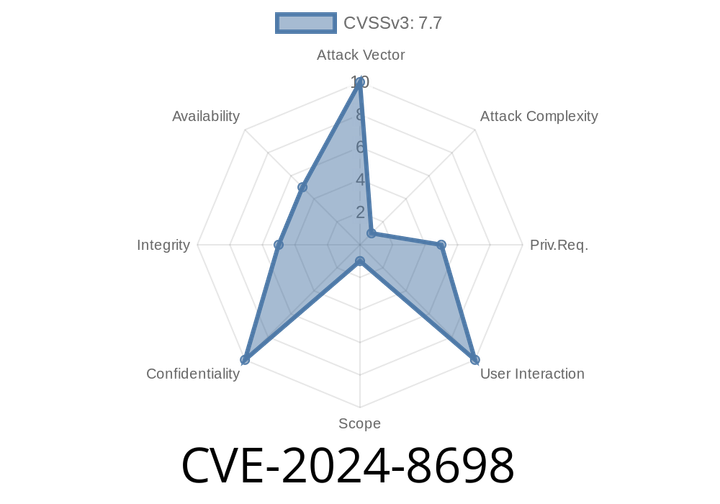
CVE-2024-8698 - How a Keycloak SAML Signature Validation Flaw Opens the Door to Impersonation
In early 2024, a significant security vulnerability was discovered in Keycloak’s handling of SAML signatures, registered as CVE-2024-8698. If your organization uses
CVE-2024-7254 - How Deeply Nested Protocol Buffers Groups Can Crash Your App—Exploiting Stack Overflow via Recursive Parsers
If your app uses Protocol Buffers to receive data—especially from untrusted sources—you must pay attention. A recently disclosed issue, tracked as CVE-2024-

CVE-2024-46771 - Linux Kernel CAN BCM Proc Entry Use-After-Remove Vulnerability Explained
In May 2024, a vulnerability—CVE-2024-46771—was fixed in the Linux kernel, affecting the Broadcast Manager (BCM) protocol for the CAN bus network
Episode
00:00:00
00:00:00