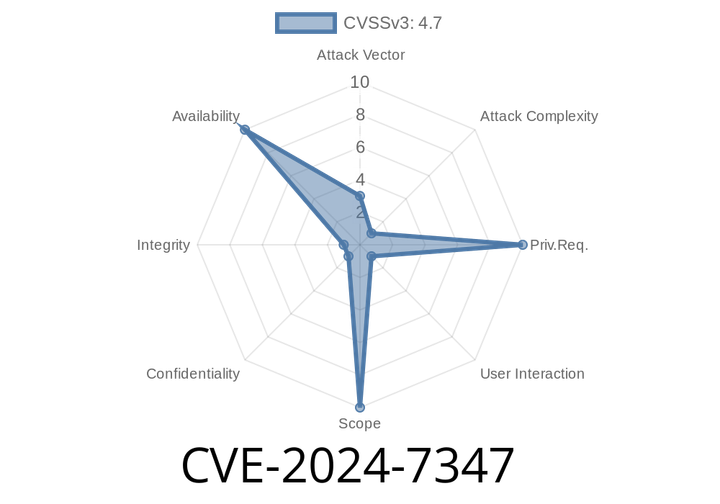
CVE-2024-7347 - Critical NGINX mp4 Module Vulnerability Explained (With Exploit Example)
NGINX is the backbone of much of the web, powering millions of sites. But sometimes, even the best software stumbles. In March 2024, a new
CVE-2024-41727 - Memory Resource Spike in BIG-IP on r200/r400 & Virtual Edition (VE) Intel E810 SR-IOV NIC — Plain English Explainer & Exploit Insights
---
What is CVE-2024-41727?
CVE-2024-41727 is a newly disclosed vulnerability affecting certain F5 BIG-IP tenants, including those running on r200 and
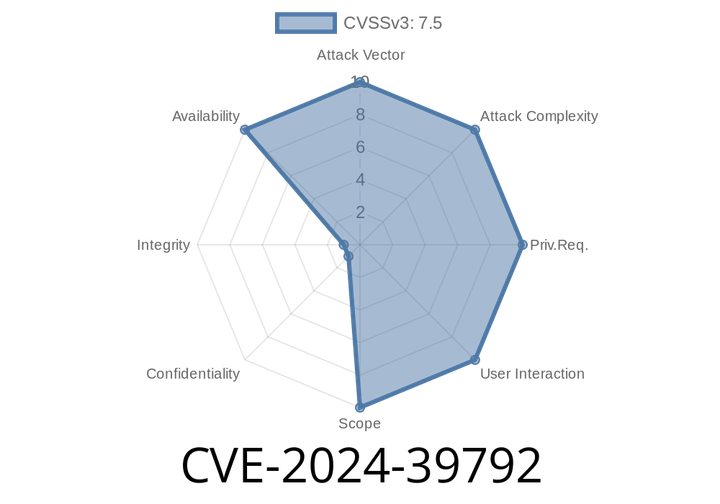
CVE-2024-39792 - How a Hidden MQTT Pre-Read Module Bug Can Crash Your NGINX Plus Server
Summary:
A security vulnerability, CVE-2024-39792, has landed in the NGINX Plus world. If you’re running this popular web server with the MQTT
CVE-2024-38163 - Windows Update Stack Elevation of Privilege Vulnerability – In-Depth Exploit Analysis
Microsoft continues its struggle to keep Windows systems secure. On June 11, 2024, they disclosed CVE-2024-38163, a high-severity Elevation of Privilege (EoP)
CVE-2024-38215 - Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Explained
On June 11, 2024, Microsoft patched a critical vulnerability known as CVE-2024-38215. In simple terms, this issue let hackers raise their system privileges
Episode
00:00:00
00:00:00