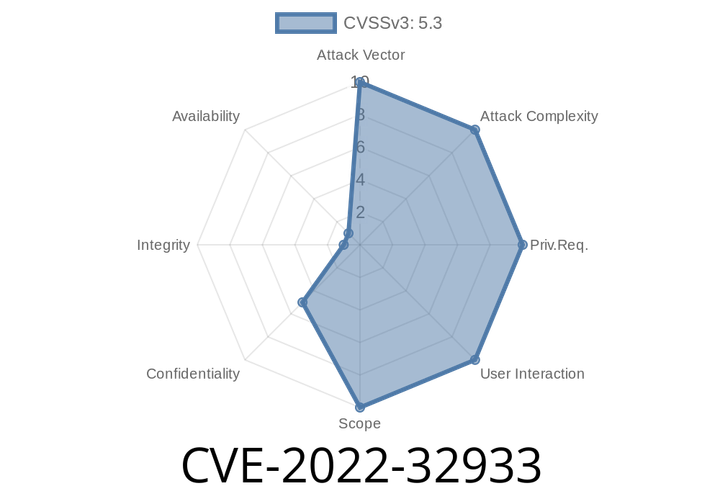
CVE-2022-32933 - How a Bug in Safari Private Browsing Mode Let Websites Track Your Browsing History
For many Apple users, Private Browsing in Safari on macOS is supposed to be just that—private. But the 2022 vulnerability tracked as CVE-2022-
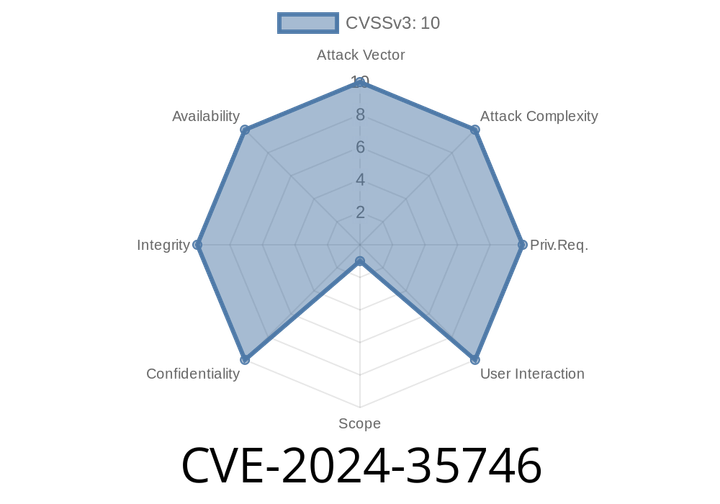
CVE-2024-35746 - Exploiting Unrestricted File Upload in BuddyPress Cover (<=2.1.4.2)
If you’re running a WordPress site with social networking features, there’s a decent chance you use the BuddyPress plugin. One popular add-on
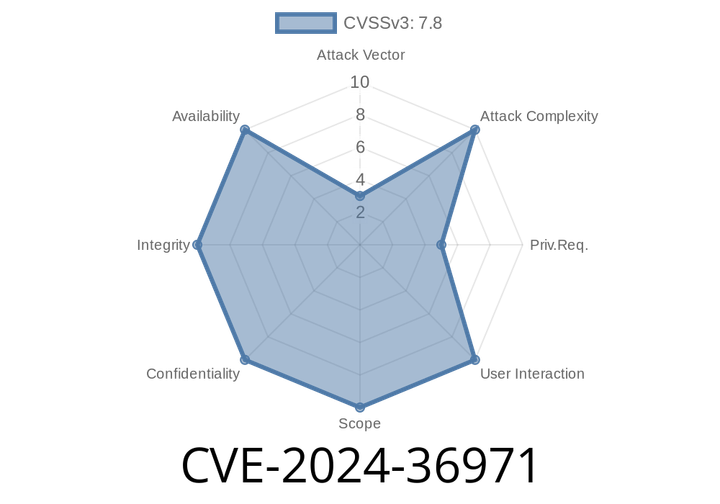
CVE-2024-36971 - Race Condition in Linux Kernel's __dst_negative_advice() Leads to Use-After-Free (UAF)
A critical race condition vulnerability—CVE-2024-36971—was discovered and patched in the Linux kernel, affecting the networking subsystem. This flaw lies in the
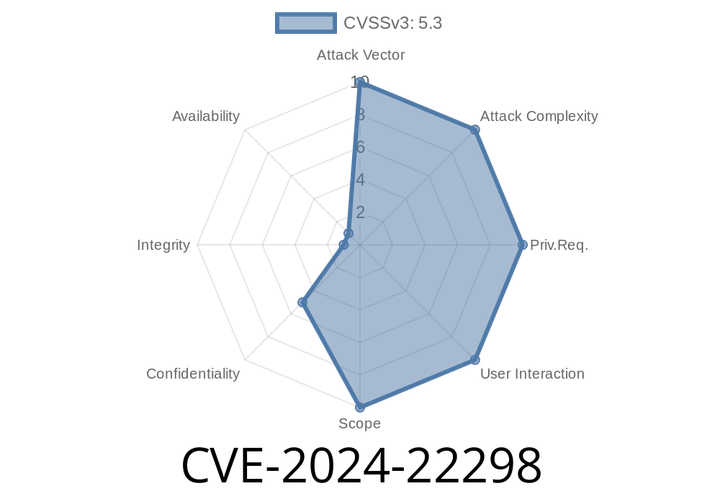
CVE-2024-22298 - Missing Authorization in TMS Amelia Bookings Plugin Can Lead to Unauthorized Access — Detailed Breakdown
In June 2024, CVE-2024-22298 was assigned to a critical security flaw found in the widely-used TMS Amelia WordPress plugin (also known as
CVE-2024-4577 - PHP CGI "Best-Fit" Unicode Encoding Flaw on Windows Lets Attackers Run Arbitrary Code
In June 2024, security researchers revealed a severe vulnerability affecting PHP when deployed through CGI under Apache on Windows. The issue, tracked as CVE-2024-
Episode
00:00:00
00:00:00