
CVE-2024-35222 - How Remote iFrames Could Hijack Your Tauri Apps Until v1.6.7 & v2..-beta.19
Tauri is a popular open-source framework for building secure, cross-platform desktop apps using web technologies — like JavaScript, HTML, and CSS. But recently, a

CVE-2024-35224 - Stored XSS (Cross-Site Scripting) in OpenProject’s Cost Report via tablesorter `{icon}` Substitution
OpenProject is a widely-used open source project management software popular in enterprises and organizations to collaborate, manage tasks, track project status, and much more.

CVE-2024-5168 - How Hackers Bypass Authentication on Prodys Quantum Audio Codec (Exclusive, Simple Explanation & Code)
A new critical security vulnerability — CVE-2024-5168 — has been discovered affecting Prodys’ Quantum Audio Codec, specifically all firmware versions up to and including 2.
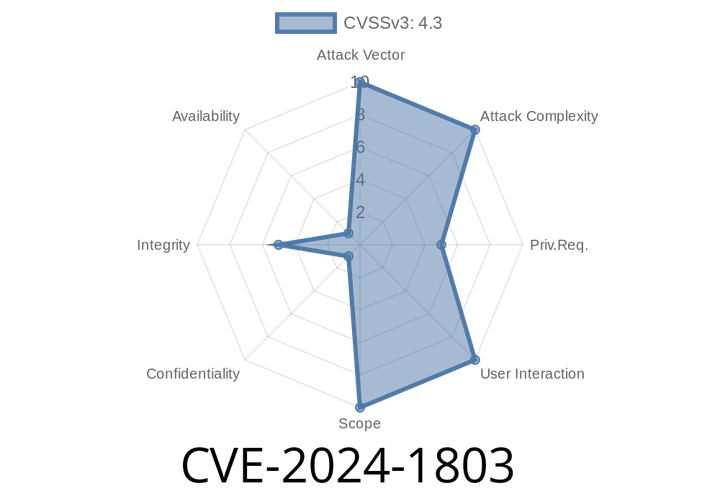
CVE-2024-1803 - Unpacking the WordPress EmbedPress PDF Block Vulnerability (Up to v3.9.12)
WordPress plugins make building and managing websites easier, but sometimes they also bring in security problems—especially when they don’t check who’s allowed
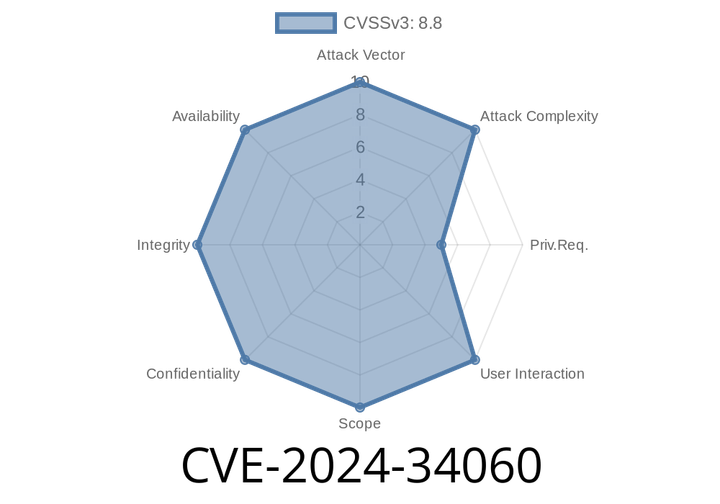
CVE-2024-34060 - Arbitrary File Write and Remote Code Execution in IrisEVTXModule Before 1..
Published: June 2024
Severity: High
Components Affected: iris-evtx-module (used by iris-web web application)
Quick Summary
A critical security flaw existed in all
Episode
00:00:00
00:00:00