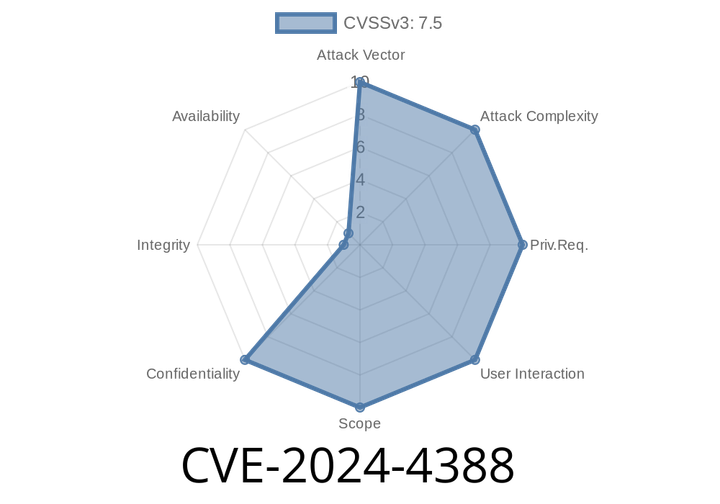
CVE-2024-4388 - Unauthenticated File Download Vulnerability Explained with PoC
A new security issue, CVE-2024-4388, has been identified, which allows attackers to download any file from a vulnerable server — without needing to log

CVE-2024-3920 - Stored Cross-Site Scripting Vulnerability in Flattr WordPress Plugin through 1.2.2
The Flattr WordPress plugin, which is widely used to monetize blogs and websites, has been discovered to have a Stored Cross-Site Scripting (XSS) vulnerability.
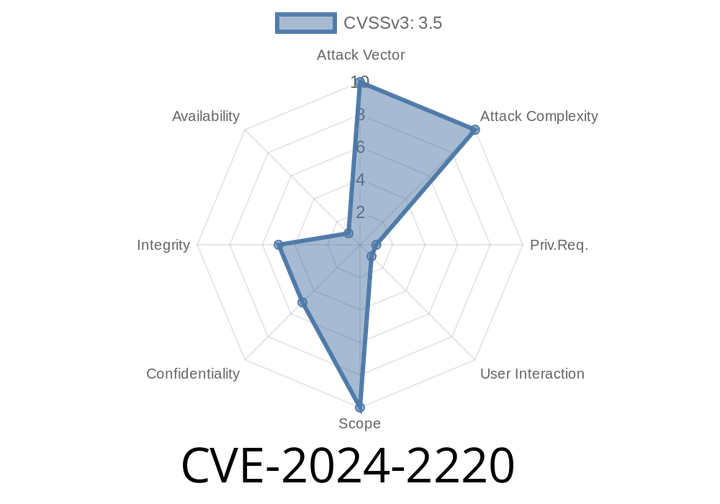
CVE-2024-2220: Stored Cross-Site Scripting (XSS) Vulnerability in Button Contact VR WordPress Plugin through 4.7
The Button Contact VR WordPress plugin (versions up to and including 4.7) is found to be vulnerable to Stored Cross-Site Scripting (XSS) attacks.
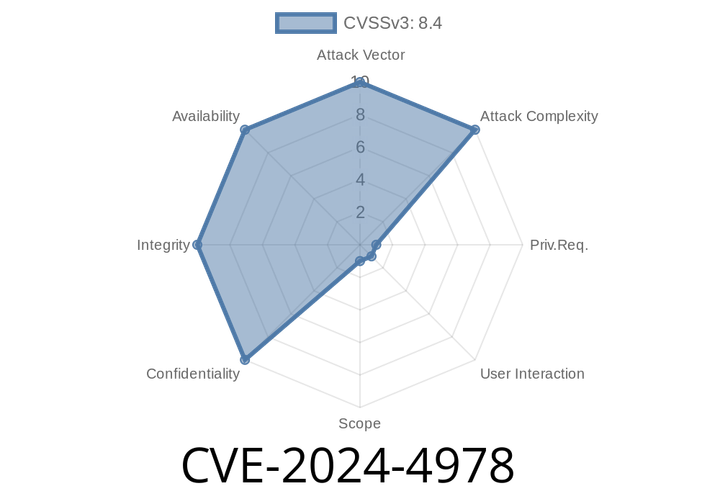
CVE-2024-4978 - Justice AV Solutions (JAVS) Viewer Setup 8.3.7.250-1 Ships Malicious Binary—How Attackers Deliver Remote PowerShell Exploits
A critical vulnerability, CVE-2024-4978, has been discovered in the *Justice AV Solutions (JAVS) Viewer* installer, specifically version 8.3.7.250-1. This
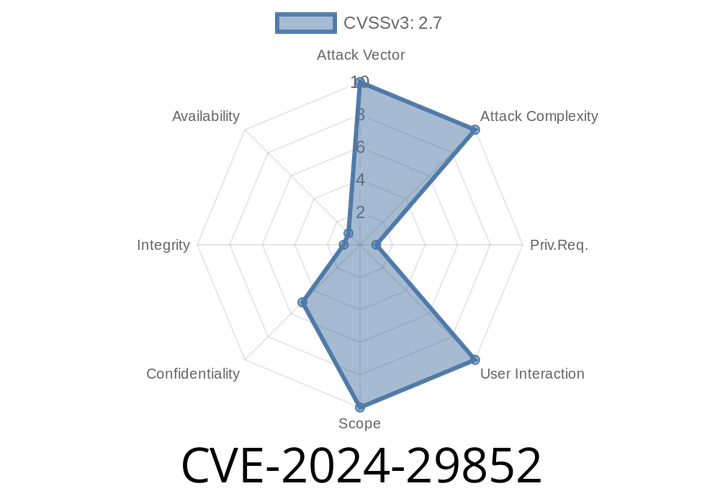
CVE-2024-29852 - High-Privileged Log Exposure in Veeam Backup Enterprise Manager
---
Veeam Backup Enterprise Manager is a popular solution for managing and monitoring Veeam Backup & Replication environments. In 2024, a new vulnerability—CVE-2024-29852—
Episode
00:00:00
00:00:00