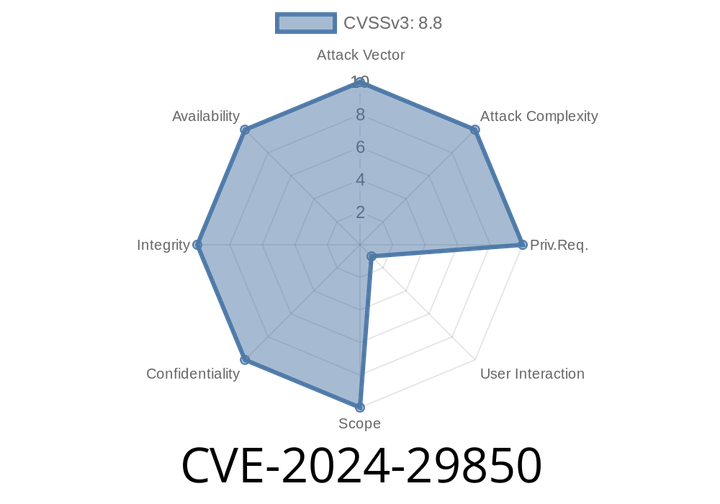
CVE-2024-29850 - Veeam Backup Enterprise Manager Account Takeover via NTLM Relay — Full Exploit & Guide
In the infosec world, authentication flaws often turn into devastating vulnerabilities. The newly disclosed CVE-2024-29850 in Veeam Backup Enterprise Manager is exactly that:
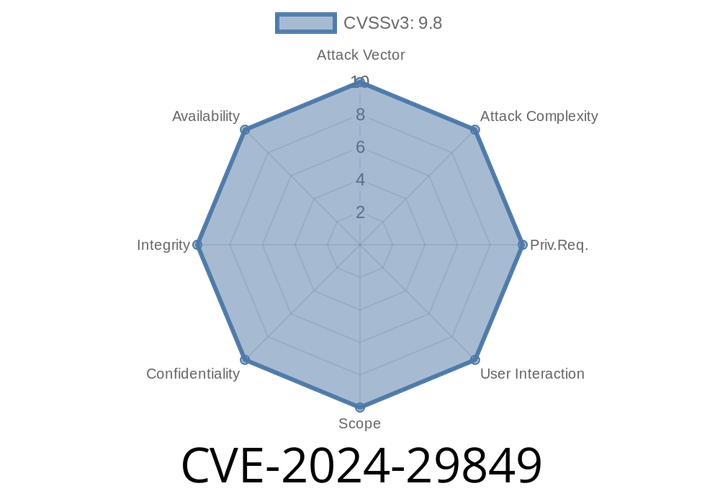
CVE-2024-29849 - Critical Veeam Backup Enterprise Manager Authentication Bypass Exploit Analysis
In May 2024, security researchers discovered a severe vulnerability in Veeam Backup Enterprise Manager that could allow attackers to bypass authentication and log in as
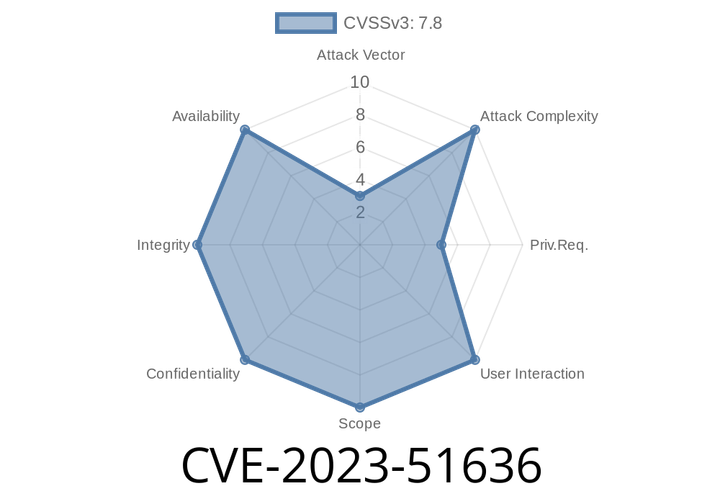
CVE-2023-51636 - Avira Prime Local Privilege Escalation Explained—How Symlinks Lead to SYSTEM Access
Cybersecurity isn’t just about stopping malware—sometimes, it's about fixing loopholes in the software meant to keep us safe. In late 2023,

CVE-2024-25738 - Critical SSRF in VuFind Lets Hackers Gain Admin Access & RCE (Full Details & Exploit)
Published: June 2024
What is CVE-2024-25738?
A new and dangerous vulnerability has come to light: CVE-2024-25738 is a Server-Side Request
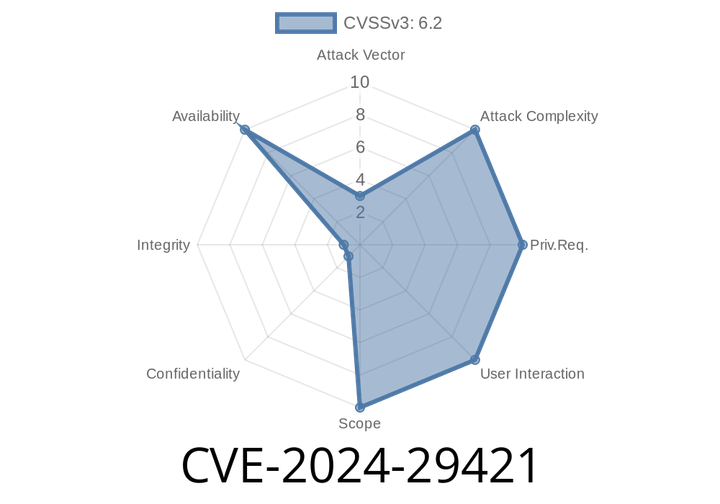
CVE-2024-29421 - Buffer Overflow in xmedcon .23. (libs/dicom/basic.c) – Details, Exploit, and Patch
CVE-2024-29421 is a critical buffer overflow vulnerability discovered in xmedcon versions up to .23., specifically in the file libs/dicom/basic.c. If
Episode
00:00:00
00:00:00