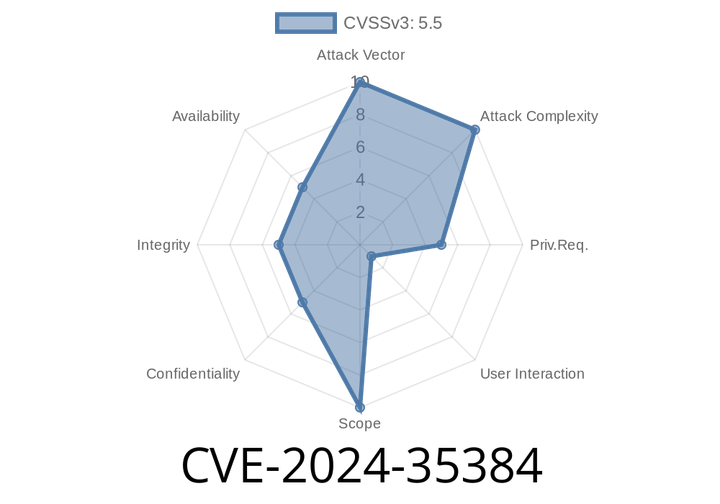
CVE-2024-35384 - Exploiting a Denial of Service in Cesanta mjs 2.20. via mjs_array_length Function
Cesanta’s mjs is a lightweight JavaScript engine designed for constrained devices, often powering microcontroller scripts and tiny IoT products. On May 2024, a new
CVE-2024-4985 - How a SAML Authentication Bypass Threatened GitHub Enterprise Server
In May 2024, a major security vulnerability was disclosed in GitHub Enterprise Server (GHES): CVE-2024-4985. This flaw specifically impacted instances using SAML Single

CVE-2024-29651 - How Prototype Pollution in json-schema-ref-parser v11../11.1. Enables Arbitrary Code Execution
---
Introduction
In March 2024, a significant security flaw was discovered in the widely-used json-schema-ref-parser library. Tracked as CVE-2024-29651, this
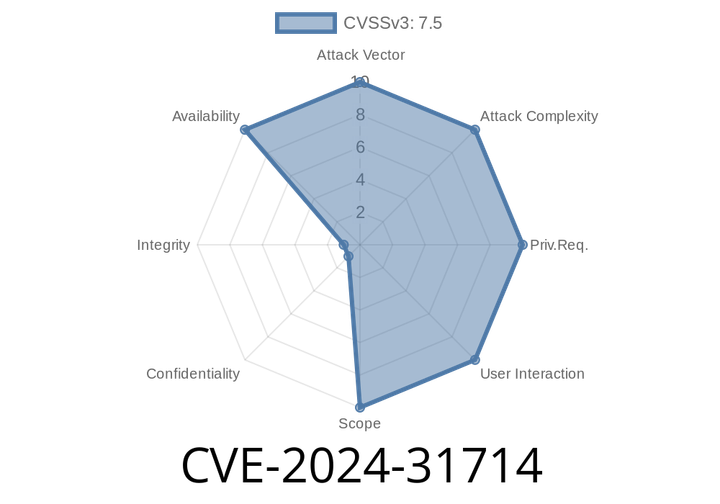
CVE-2024-31714 - Buffer Overflow in Waxlab Wax .9-3 and Earlier Lets Attackers Crash Apps with Lua
Security vulnerabilities in open source software aren’t just for the big names — sometimes a smaller project like Waxlab's "wax" can

CVE-2024-34949 - Critical SQL Injection in Likeshop Affects Order Management (Exploit and Analysis)
A new critical vulnerability, CVE-2024-34949, has been identified in Likeshop before version 2.5.7. This security flaw allows attackers to run arbitrary
Episode
00:00:00
00:00:00