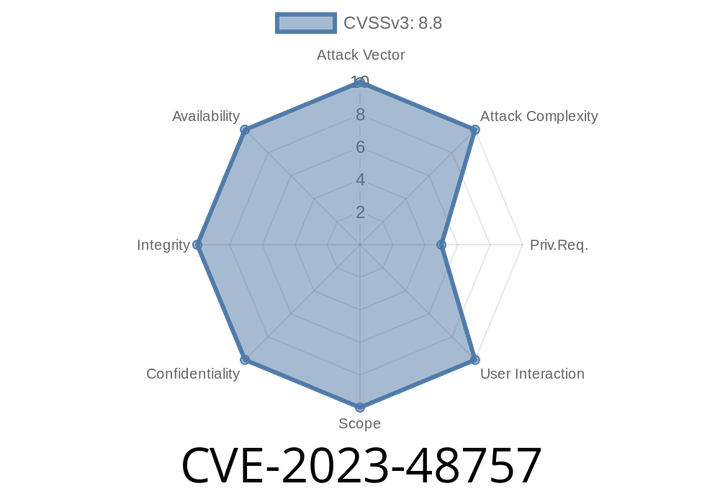
CVE-2023-48757 - Privilege Escalation in Crocoblock JetEngine (<= 3.2.4) Explained with Exploit Details
A serious security vulnerability tagged as CVE-2023-48757 was found in Crocoblock JetEngine, a popular WordPress plugin for building dynamic websites. This post is
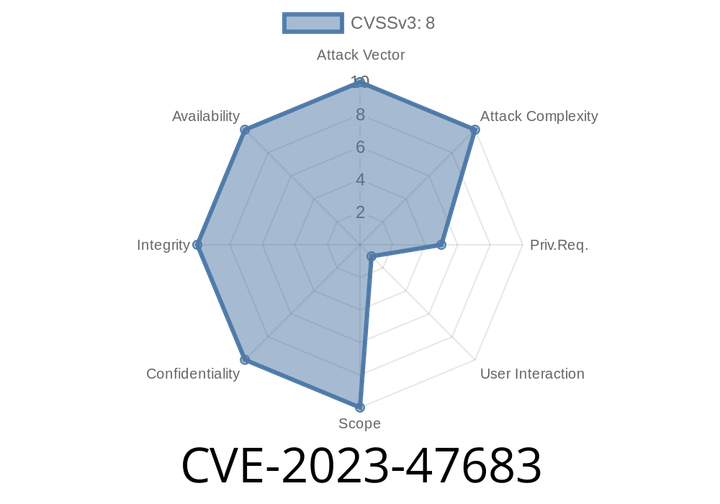
CVE-2023-47683 - How a MiniOrange WordPress Social Login Flaw Enables User Privilege Escalation (With Exploit Details)
On November 20, 2023, CVE-2023-47683 was assigned to a critical vulnerability in the widely used WordPress Social Login and Register plugin by miniOrange.
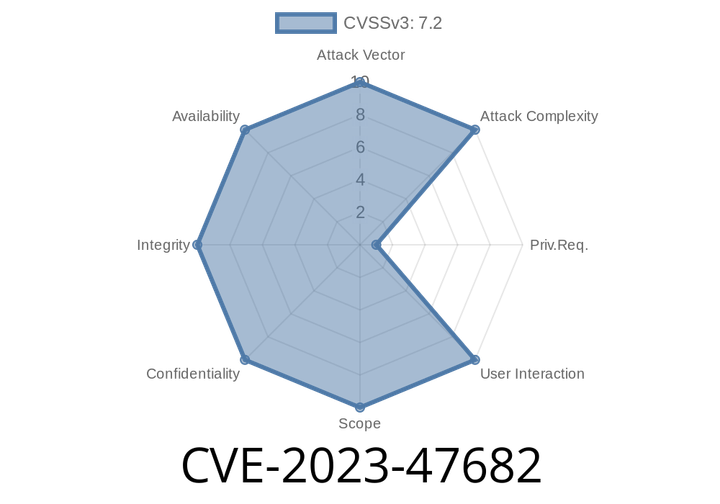
CVE-2023-47682 - How a Privilege Escalation Bug in WP User Frontend Lets Attackers Take Over WordPress Sites
WordPress plugins often make life easier, but they can also introduce nasty vulnerabilities. In this post, we’ll unpack CVE-2023-47682, a privilege escalation

CVE-2023-47679 - Critical Path Traversal Vulnerability in QODE Interactive Qi Addons For Elementor (<= 1.6.3)
A serious security vulnerability, CVE-2023-47679, affects the popular WordPress plugin Qi Addons For Elementor by QODE Interactive. If you use Elementor and manage

CVE-2023-46784 - Path Traversal and SSRF in ICS Calendar (Room 34 Creative Services) – Vulnerability Explained and Exploited
A serious vulnerability, CVE-2023-46784, has been reported in the ICS Calendar WordPress plugin by Room 34 Creative Services, LLC. This vulnerability exposes websites
Episode
00:00:00
00:00:00