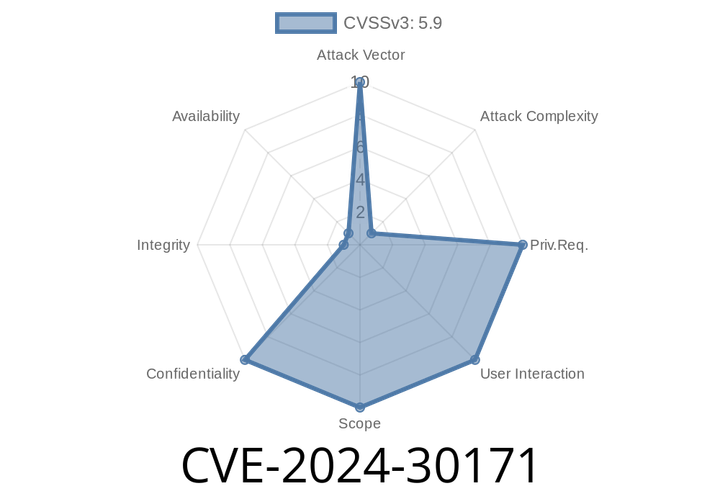
CVE-2024-30171 - Timing Attack Risk in Bouncy Castle’s Java TLS API and JSSE Provider – Explained, Exploited, and Patched
Bouncy Castle is one of the most trusted libraries for cryptographic operations in Java. Used by developers and organizations worldwide, its TLS API and JSSE
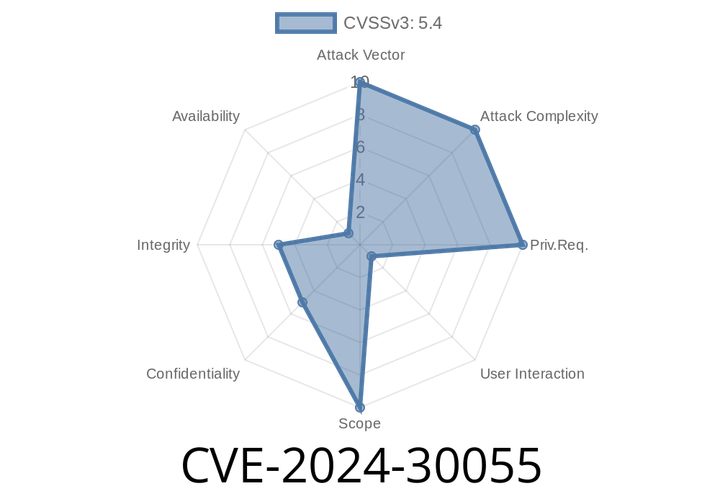
CVE-2024-30055 - Inside the Microsoft Edge (Chromium-based) Spoofing Vulnerability
---
Microsoft Edge is one of the most widely used browsers, especially in workplace environments. It’s fast, secure, and built on Chromium — the same core
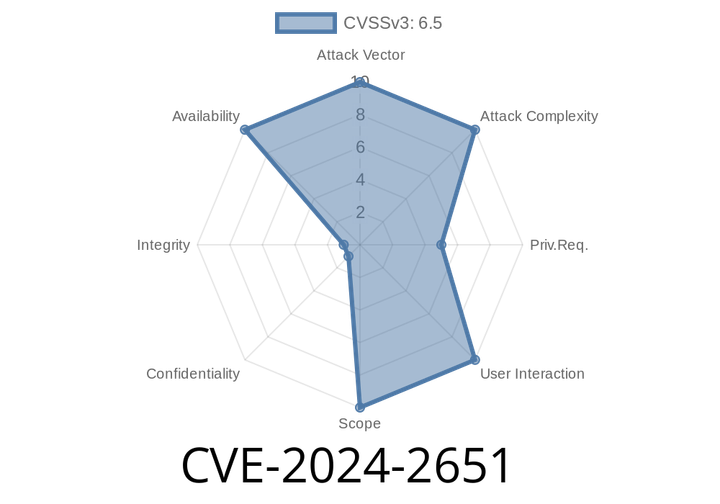
CVE-2024-2651 - Exploiting a GitLab Markdown Denial-of-Service Vulnerability (Exclusive Guide)
A major security flaw, CVE-2024-2651, was discovered in GitLab’s popular CE/EE products. This bug lets attackers crash GitLab by simply using

CVE-2024-2454 - Critical DoS Vulnerability in GitLab CE/EE’s Pins Endpoint - How It Works and How to Mitigate
GitLab is a favorite tool for developers worldwide, used for code collaboration and DevOps workflows. But like any popular platform, it can attract security issues.

CVE-2024-29857 - Exploiting Excessive CPU Usage in Bouncy Castle ECCurve Certificate Parsing
CVE-2024-29857 is a recently disclosed vulnerability affecting a family of cryptographic libraries known as Bouncy Castle. This issue revolves around how the libraries
Episode
00:00:00
00:00:00