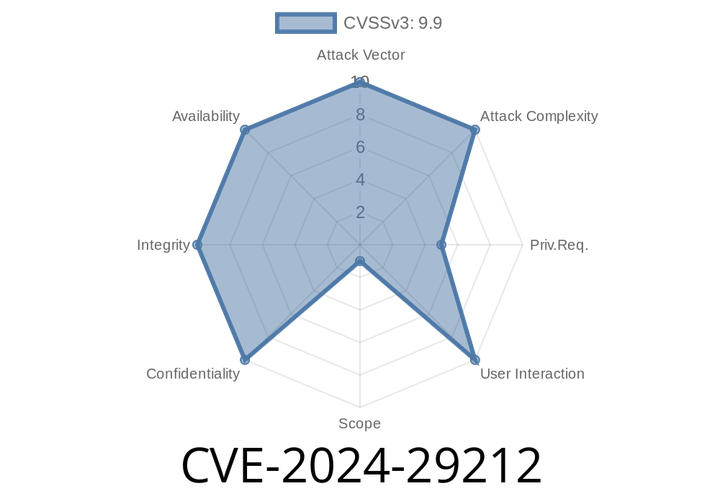
CVE-2024-29212 - Remote Code Execution in Veeam Service Provider Console via Unsafe Deserialization
CVE-2024-29212 is a critical vulnerability in Veeam Service Provider Console (VSPC) that could allow an attacker to perform Remote Code Execution (RCE) on

CVE-2024-29157 - Heap Buffer Overflow in HDF5’s H5HG_read – Understanding, Exploit, and Mitigation
On June 2024, a security weakness identified as CVE-2024-29157 was discovered in the HDF5 library up to version 1.14.3. HDF5 (Hierarchical

CVE-2024-28761 - IBM App Connect Enterprise HTML Injection Exploit – All You Need to Know
CVE-2024-28761 is a recently disclosed security vulnerability impacting IBM App Connect Enterprise (ACE), versions 11...1 through 11...25 and 12..1. through
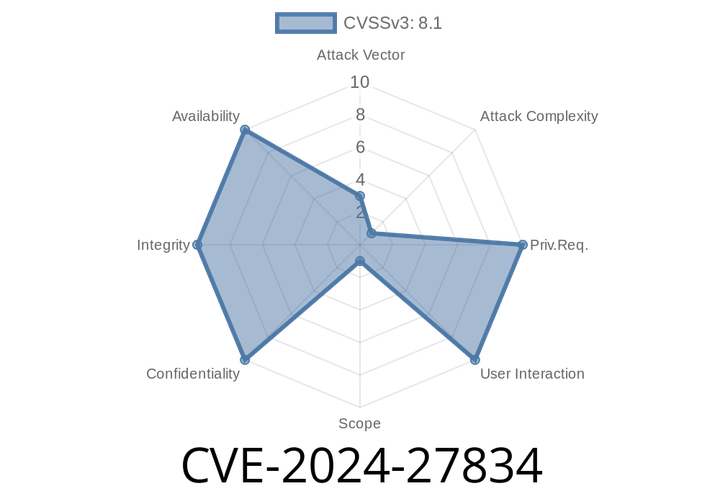
CVE-2024-27834 - Understanding and Exploiting the Apple Pointer Authentication Bypass
Apple security vulnerabilities don’t make big headlines every day. But when one lets attackers bypass memory protections put in place to stop hacking at

CVE-2024-27822 - Exploring the macOS Sonoma 14.5 Root Privilege Escalation Bug
On May 13, 2024, Apple released macOS Sonoma 14.5, quietly patching a critical vulnerability assigned CVE-2024-27822. This post provides an exclusive deep-
Episode
00:00:00
00:00:00