CVE-2024-4438 - Rapid Reset Redux in Red Hat OpenStack’s etcd Package – Incomplete Patch Risks
*Published: June 2024 | Author: SecureBytes Blog Team*
Summary:
A recent CVE—CVE-2024-4438—reveals a security gap in the etcd package distributed with the
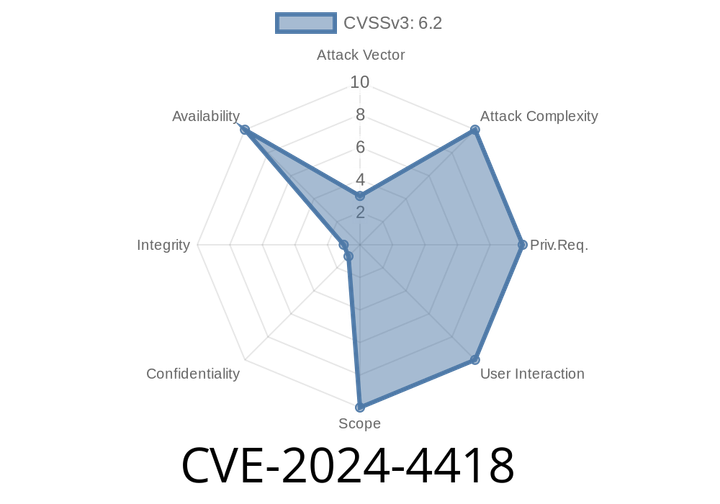
CVE-2024-4418 - Race Condition Leads to Stack Use-After-Free in libvirt (Exploit Details and Analysis)
On May 2024, security researcher Ziming Zhang from Ant Security discovered CVE-2024-4418, a severe race condition in libvirt, an essential component for managing

CVE-2023-27321 - Easy Exploit in OPC UA .NET Standard with ConditionRefresh – Resource Exhaustion and Denial-of-Service Explained
The Industrial Internet-of-Things (IIoT) is all about automation and connectivity, and at the heart of many automation systems sits OPC UA. Millions around
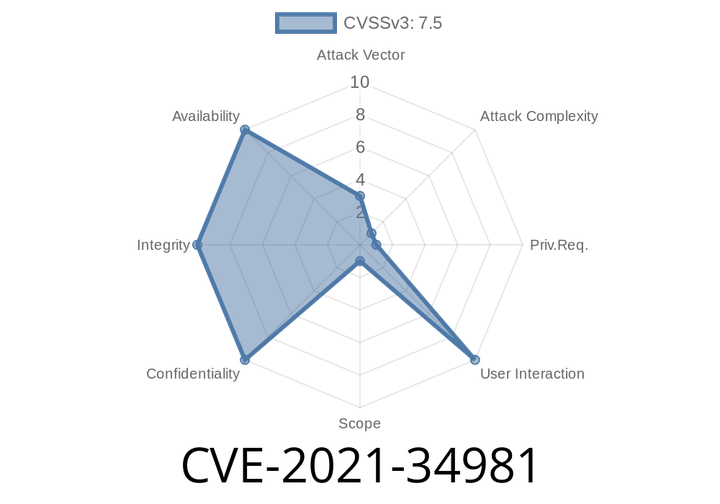
CVE-2021-34981 - Linux Kernel Bluetooth CMTP Module Double Free Privilege Escalation Vulnerability Explained
In July 2021, a new high-severity Linux kernel vulnerability came to light as CVE-2021-34981 (also tracked as ZDI-CAN-11977). This vulnerability

CVE-2024-23713 - Local Privilege Escalation in Android NotificationManagerService – Analysis, Code, and Exploit Details
---
Android is the world’s most popular mobile operating system, and with its popularity comes continuous scrutiny from the security community. One of the newly
Episode
00:00:00
00:00:00