
CVE-2024-23710 - How a Logic Error in Android's Package Management Can Let Attackers Gain Privileges
CVE-2024-23710 is a recently disclosed security vulnerability affecting the Android operating system. Specifically, the bug lies in the assertPackageWithSharedUserIdIsPrivileged method within InstallPackageHelper.java.

CVE-2024-0042 - How Certificate Confusion in TBD’s DRM Lets Attackers Bypass Content Protection
A recently disclosed vulnerability, CVE-2024-0042, in the nebulously-named “TBD” of “TBD” (pending official confirmation, but possibly a major DRM-enabled platform), has
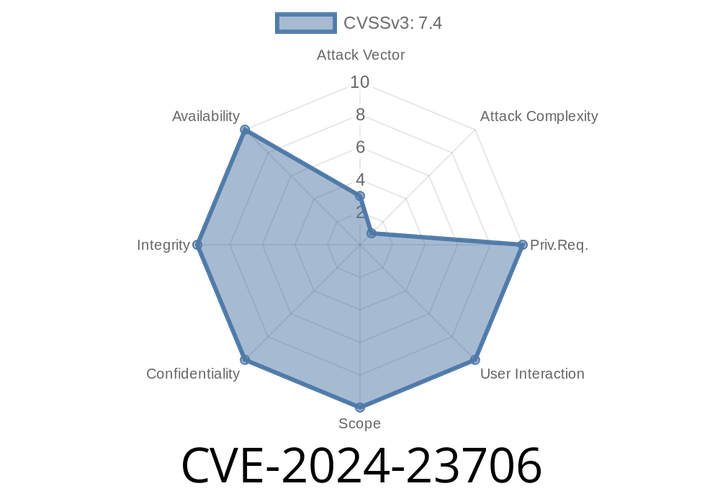
CVE-2024-23706 - Health Data Permission Bypass Leads to Local Privilege Escalation – A Deep Dive
Security vulnerabilities that let attackers bypass key permissions and access sensitive data are always concerning. But when these involve health data, the impact rapidly turns
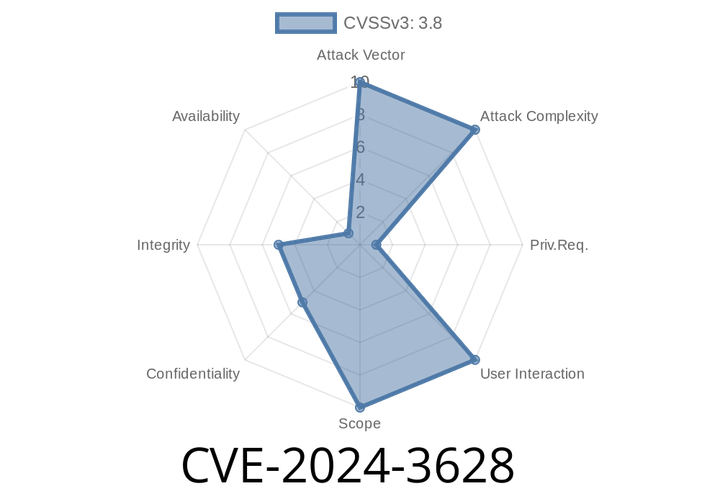
CVE-2024-3628 - EasyEvent WordPress Plugin XSS Vulnerability Explained (with Exploit Example)
WordPress is the world's most popular content management system, but even the best plugins can have dangerous security issues. One recent case is
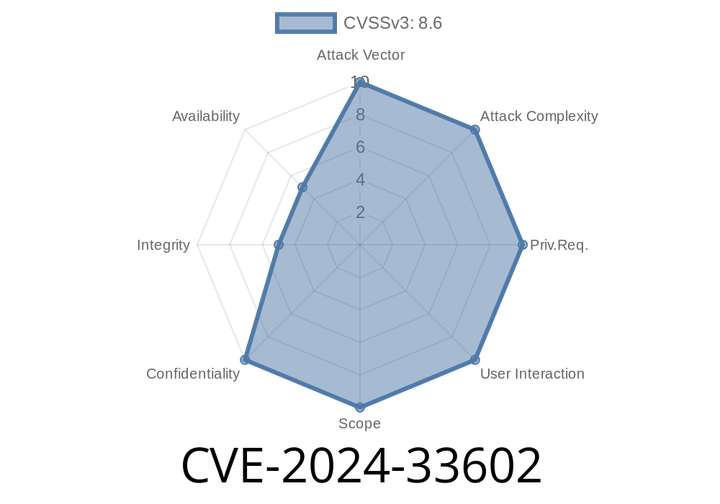
CVE-2024-33602 - Breaking Down the netgroup Cache Vulnerability in nscd (glibc)
In short:
A memory corruption bug was discovered in the nscd (Name Service Cache Daemon) component of glibc—specifically in the netgroup cache logic. By
Episode
00:00:00
00:00:00