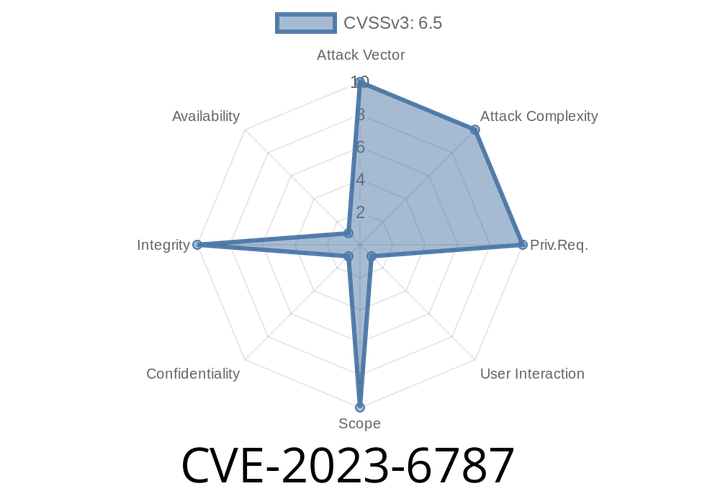
CVE-2023-6787 - Keycloak Session Hijacking via Re-authentication Flaw
Keycloak is a popular open-source identity and access management tool used by many organizations to secure their web applications. However, in December 2023, a
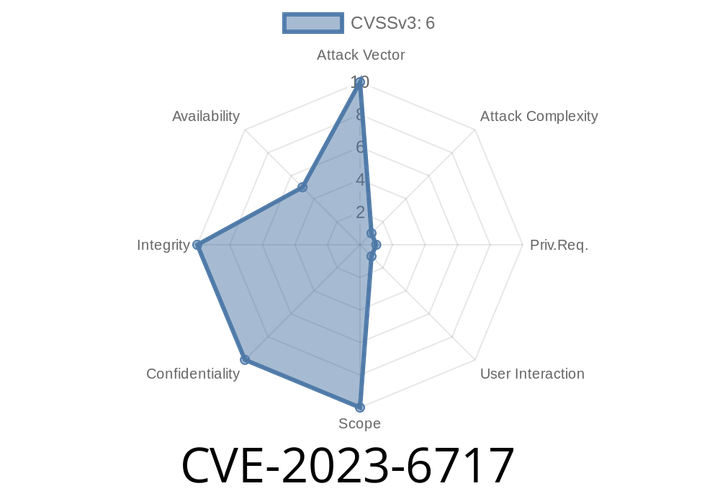
CVE-2023-6717 - Keycloak SAML Client Registration Flaw Exposes JavaScript XSS Attack
Date: June 2024
Author: [Your Name]
Tags: Keycloak, SAML, CVE-2023-6717, XSS, Security, Exploit
Overview
A vulnerability, tracked as CVE-2023-6717, has been

CVE-2023-6484 - Log Injection Vulnerability in Keycloak WebAuthn Explained (with Code Example & Exploit Details)
Keycloak is an open-source software solution for identity and access management, used worldwide to secure web apps and services. In January 2024, a new
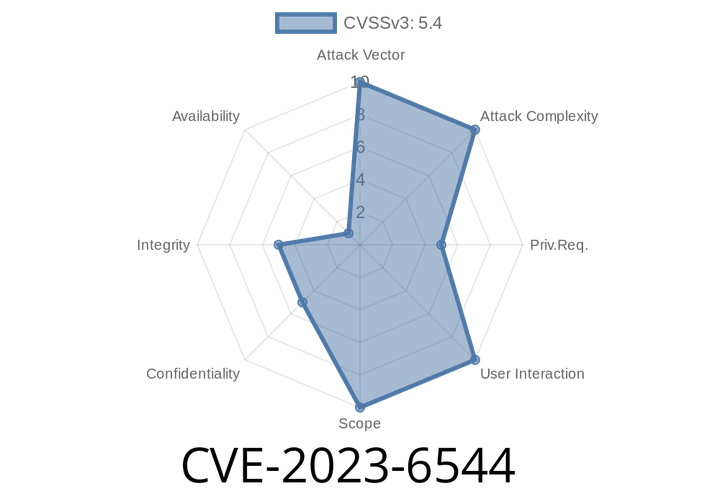
CVE-2023-6544 - Exploiting a Dangerous Regex in Keycloak’s Dynamic Client Registration
Keycloak is a widely used open-source identity and access management (IAM) solution for modern applications and services. It helps companies manage authentication, authorization, and
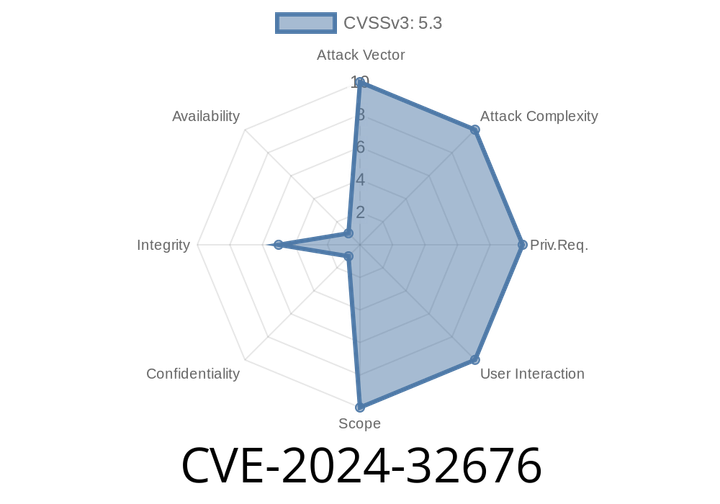
CVE-2024-32676 - How LoginPress Pro’s Authentication Bug Can Shut Down Key Login Features
*Published: June 2024*
*Author: [Your Name]*
Introduction
A critical vulnerability, CVE-2024-32676, was recently found in the popular WordPress plugin LoginPress Pro. This flaw,
Episode
00:00:00
00:00:00