
CVE-2024-31077 - Deep Dive Into Forminator Plugin SQL Injection Vulnerability
Forminator is a popular WordPress plugin designed to help users quickly build forms, polls, and quizzes. But in early 2024, security researchers discovered a major

CVE-2024-28890 - How Forminator's File Upload Vulnerability Puts Your WordPress Site at Risk
---
Executive Summary
CVE-2024-28890 affects the popular WordPress plugin Forminator prior to version 1.29.. The core problem? Anyone could upload dangerous files—think
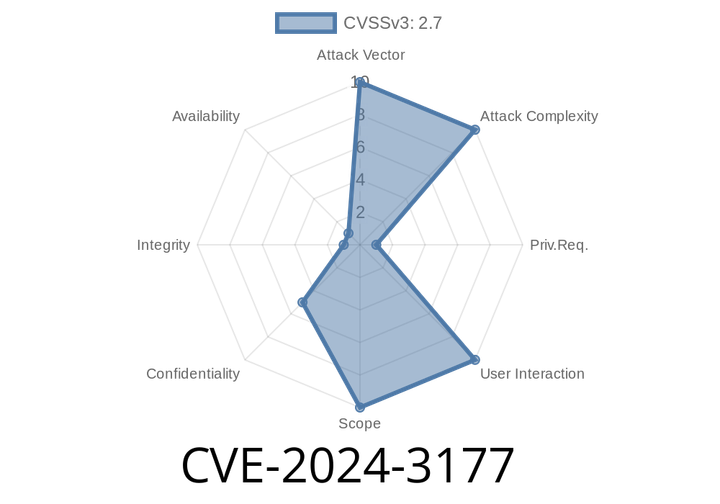
CVE-2024-3177 - Bypassing Kubernetes Mountable Secrets Policy via envFrom Field
CVE-2024-3177 points to a significant security issue in Kubernetes. This vulnerability lets users launch containers that can sidestep the “mountable secrets” restrictions on
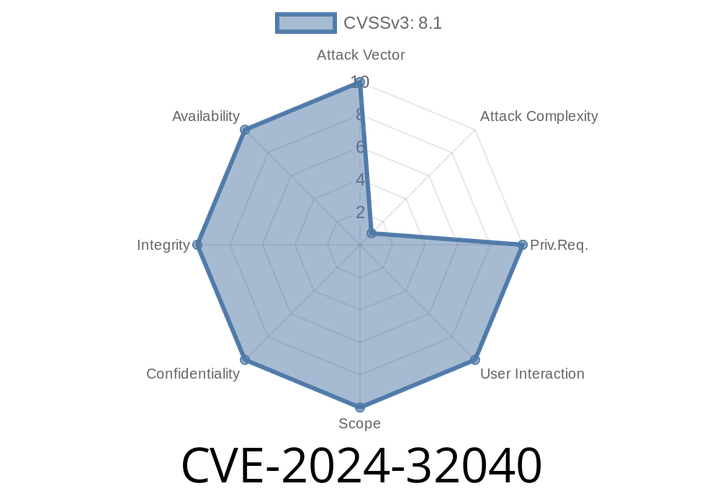
CVE-2024-32040 - FreeRDP NSC Codec Integer Underflow Vulnerability – Simple Explanation, Code Example, and Exploit Details
FreeRDP is a popular open-source implementation of the Remote Desktop Protocol (RDP), used in many third-party remote desktop clients. In May 2024, a

CVE-2024-4040: Server Side Template Injection Vulnerability in CrushFTP Allows Unauthenticated Remote Attackers to Perform Remote Code Execution and Bypass Authentication
The latest cyber security vulnerability CVE-2024-4040 affects all CrushFTP versions before 10.7.1 and 11.1. on all platforms, potentially exposing systems
Episode
00:00:00
00:00:00