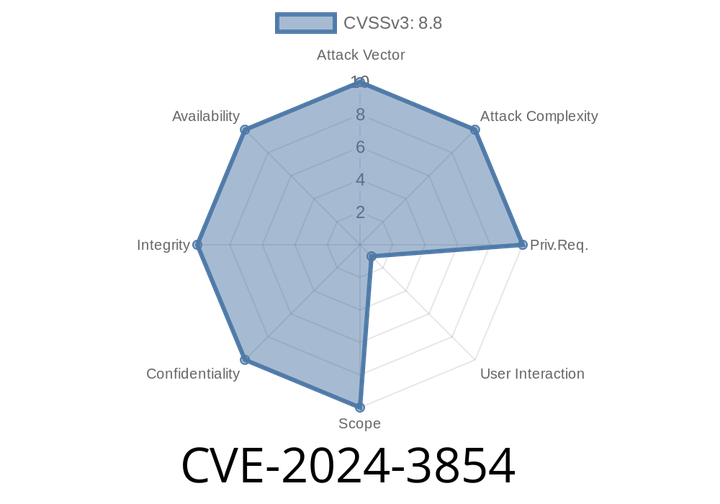
CVE-2024-3854 - Firefox JIT Switch Statement Bug Leads to Out-of-Bounds Reads
If you use Firefox, Firefox ESR, or Thunderbird, there’s a new vulnerability you need to know about — CVE-2024-3854. This bug can let

CVE-2024-31990 - How a Security Hole in Argo CD Let Attackers Edit Kubernetes Resources
Argo CD is a leading open-source GitOps tool that lets you manage your Kubernetes resources by tracking them in Git. If you run modern
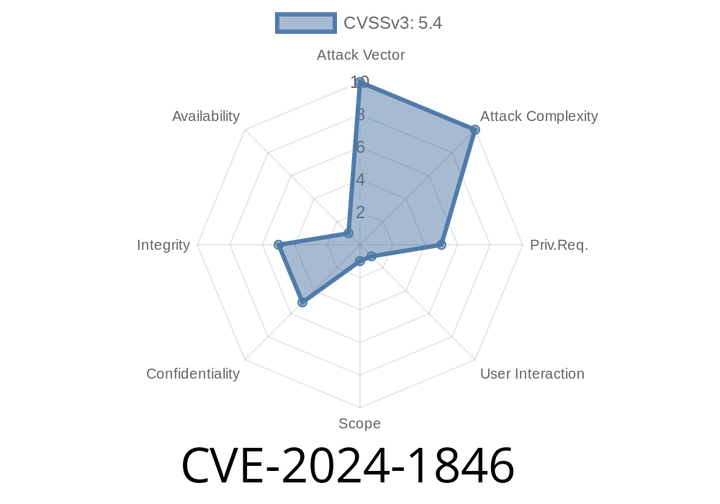
CVE-2024-1846 - Exploiting Stored XSS in the Responsive Tabs WordPress Plugin (Pre-4..7) – Full Walkthrough and Proof-Of-Concept
CVE-2024-1846 is a vulnerability found in the popular Responsive Tabs WordPress plugin. This vulnerability affects all plugin versions before 4..7. The problem?
CVE-2024-1310: Unauthorized Product Data Leakage in WooCommerce WordPress Plugin Before 8.6 - Exploit Details and Recommended Security Measures
Are you using the WooCommerce WordPress plugin to run your e-commerce site? If your installed version is before 8.6, your site may be
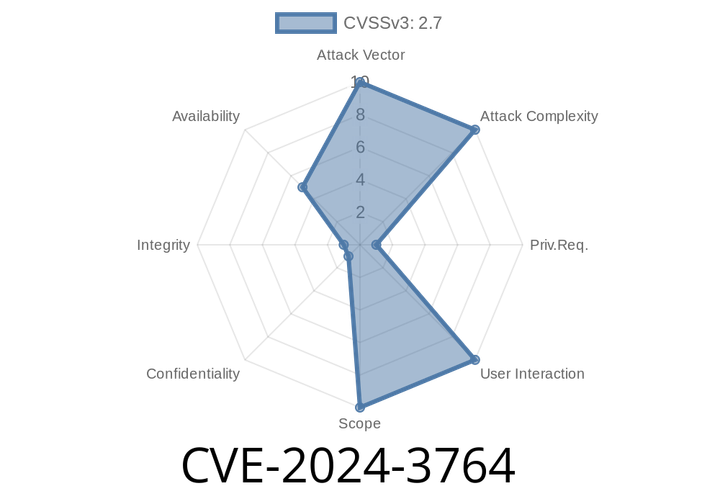
CVE-2024-3764 - Understanding the **DISPUTED** Tuya MQTT Packet Handler Denial of Service Issue
---
Introduction
In June 2024, a controversial vulnerability surfaced involving the Tuya Embedded SDK (versions up to 5..x) in its MQTT Packet Handler component. Labeled
Episode
00:00:00
00:00:00