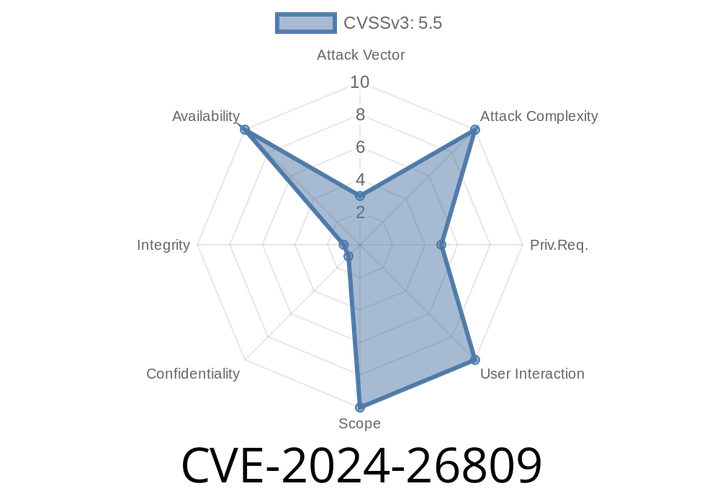
CVE-2024-26809 - Double Free Vulnerability Fixed in Linux Kernel’s nft_set_pipapo
In March 2024, security researchers and kernel developers identified and patched a vulnerability in the Linux kernel’s netfilter subsystem, specifically involving nft_set_pipapo.
CVE-2024-3272 - Critical D-Link NAS Bug Exposes Hard-Coded Credentials – Exploit Guide & Full Details
In early April 2024, a severe security flaw—CVE-2024-3272—shook the old-but-still-used D-Link NAS family: DNS-320L, DNS-325,
CVE-2024-3273 - Critical Command Injection Vulnerability in Legacy D-Link NAS Devices (DNS-320L, 325, 327L, 340L)
_Discovered: April 2024_
_Affected Models: D-Link DNS-320L, DNS-325, DNS-327L, DNS-340L (Up to 20240403)_
_Reference: VDB-259284_
_Exploit Status: Public_
What

CVE-2024-31390 - Exploiting Code Injection in Breakdance Page Builder (All Versions up to 1.7.1)
If you work with WordPress page builders, you may have heard of Breakdance, a popular drag-and-drop tool from Soflyy. In early 2024, a
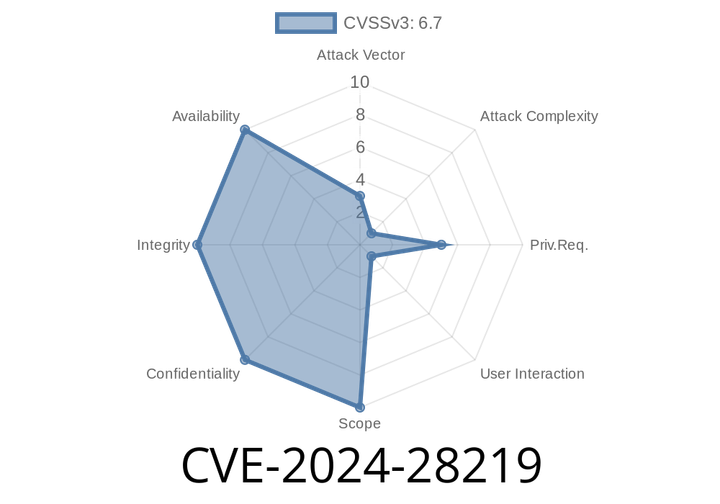
CVE-2024-28219 - Critical Buffer Overflow in Pillow’s _imagingcms.c (Exploit & Analysis)
On March 21, 2024, the popular Python imaging library Pillow patched a serious security bug in their C extension: CVE-2024-28219. This vulnerability affects
Episode
00:00:00
00:00:00