
CVE-2023-6090 - Unrestricted Upload of File with Dangerous Type Vulnerability in Mollie Payments for WooCommerce
In recent times, there has been a surge in security breaches in the e-commerce sector. In the wake of these events, we have discovered
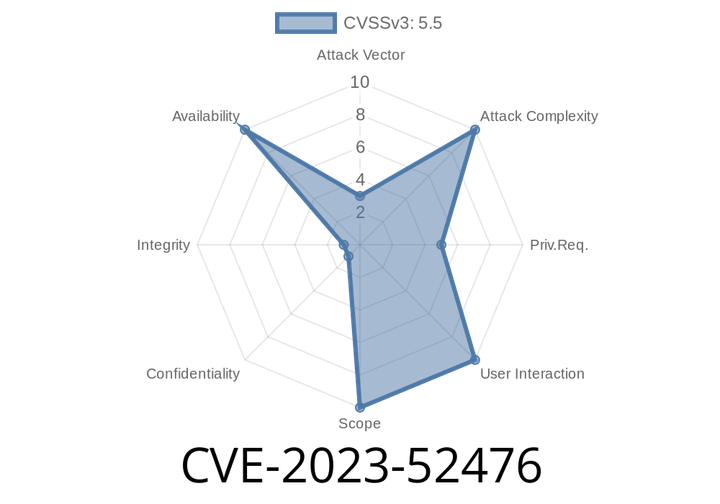
CVE-2023-52476 - Critical Linux Kernel Vulnerability in perf/x86 LBR – Exploit Details and Patch Review
A major vulnerability, CVE-2023-52476, was recently resolved in the Linux kernel’s x86 performance event (perf) subsystem. If you run kernels with perf

CVE-2023-1841 - XSS Vulnerability in Honeywell MPA2 Access Panel – How It Works and How to Protect Yourself
Honeywell's MPA2 Access Panel is a popular product for managing access control in buildings and secure environments. However, in early 2023, cybersecurity researchers
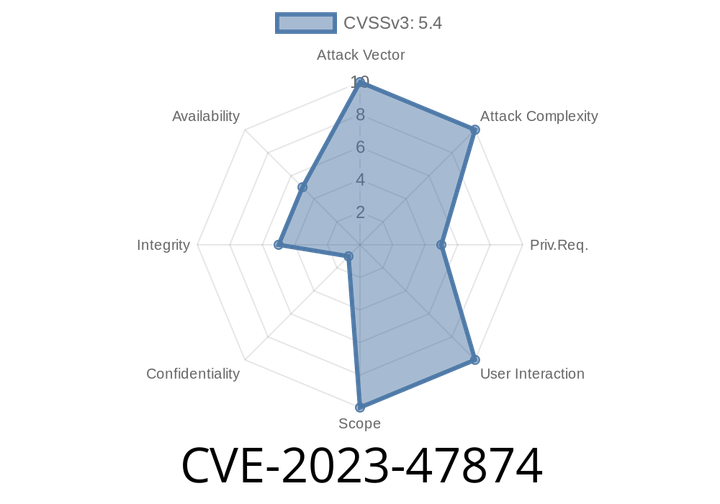
CVE-2023-47874 - Missing Authorization in Perfmatters WordPress Plugin (<= 2.1.6) — How Attackers Can Exploit It
On October 30, 2023, a serious vulnerability was disclosed in the popular Perfmatters WordPress plugin—an optimization tool used on over 100,000 WordPress sites.
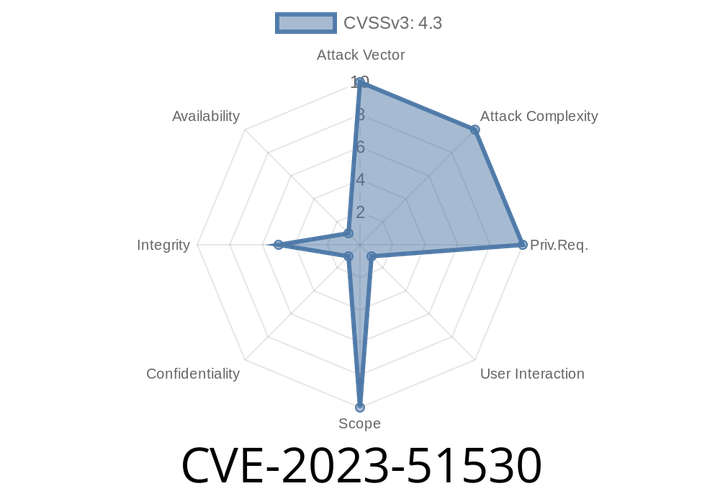
CVE-2023-51530 - Exploiting CSRF in GS Plugins Logo Slider – Showcase Your Logos, Expose Your Site
Summary:
*CVE-2023-51530* is a Cross-Site Request Forgery (CSRF) vulnerability found in the WordPress plugin Logo Slider – Logo Showcase, Logo Carousel, Logo Gallery
Episode
00:00:00
00:00:00