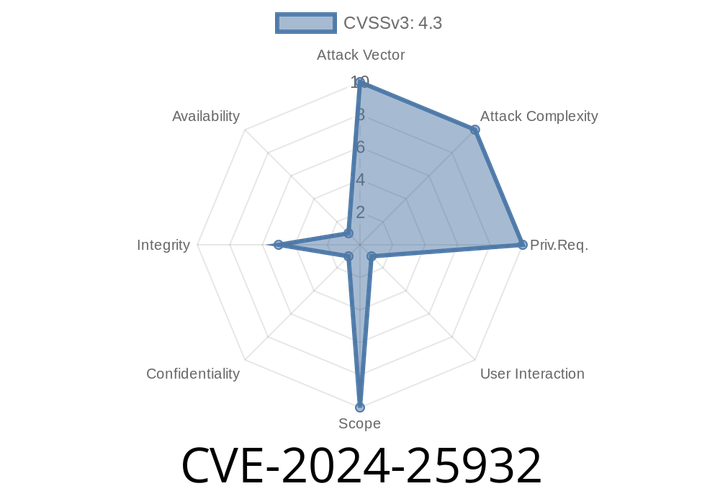
CVE-2024-25932 - How CSRF Left Change Table Prefix WordPress Plugin Wide Open (Full Exploit Walkthrough)
On February 2024, the cybersecurity community uncovered a serious Cross-Site Request Forgery (CSRF) vulnerability, tracked as CVE-2024-25932, in the popular *Change Table

CVE-2024-25832 - Unrestricted File Upload in F-logic DataCube3 v1. Explained
In early 2024, a new vulnerability was discovered in F-logic DataCube3 v1.—a data analysis and visualization web application. Tracked as CVE-2024-25832,
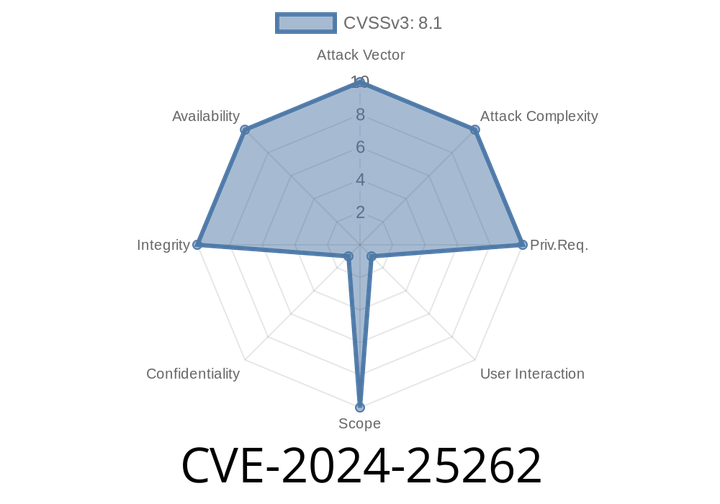
CVE-2024-25262 - Heap Buffer Overflow in texlive-bin’s ttfdump (ttfLoadHDMX) – Denial of Service via Crafted TTF Files
In early 2024, a serious vulnerability—CVE-2024-25262—was discovered in the texlive-bin package, specifically in its ttfdump utility as maintained by commit
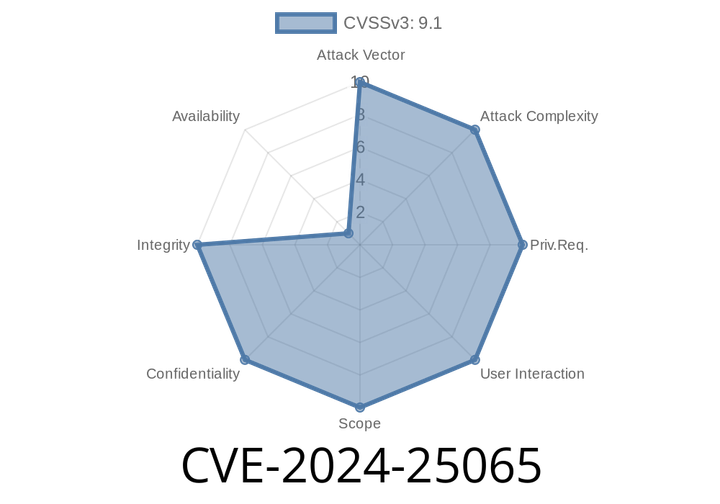
CVE-2024-25065 - Path Traversal in Apache OFBiz—Exploit Details, Simple Explanation & How to Stay Safe
A new security flaw has been found in Apache OFBiz, an open-source enterprise automation platform. Labeled CVE-2024-25065, this critical vulnerability lets attackers
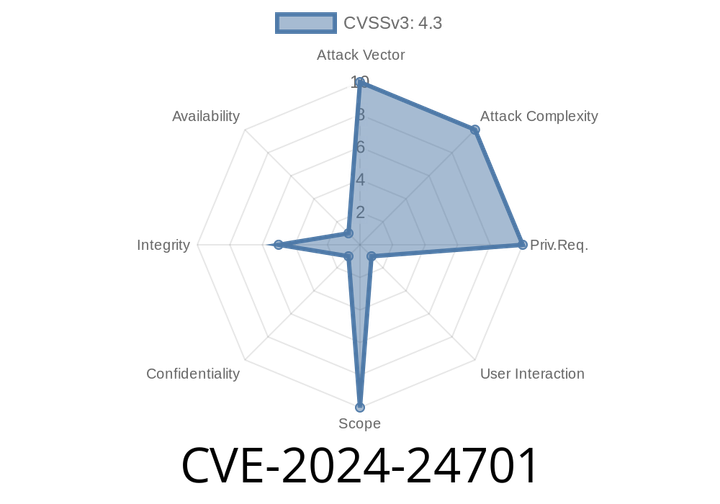
CVE-2024-24701 - How a CSRF Bug Threatens Websites Using Native Grid’s No-Code Page Builder (v2.1.20 and Below)
On February 2024, a pretty dangerous vulnerability popped up in Native Grid LLC’s “A no-code page builder for beautiful performance-based content”. Tracked
Episode
00:00:00
00:00:00