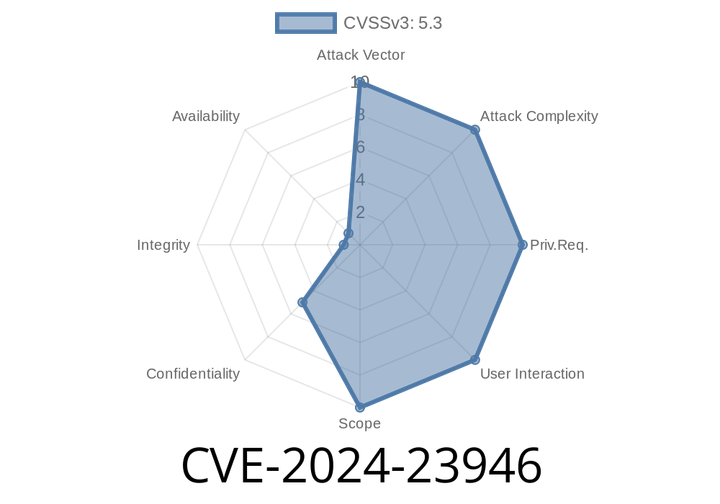
CVE-2024-23946 - Path Traversal Flaw in Apache OFBiz Leads to Arbitrary File Inclusion
---
Apache OFBiz is an open-source enterprise resource planning (ERP) and e-commerce software widely used by businesses to run backend operations. On January 29,

CVE-2024-24147 - Memory Leak in libming v.4.8 parseSWF_FILLSTYLEARRAY Enables DoS via Malicious SWF File
---
Overview
A recent security flaw, CVE-2024-24147, has been identified in libming v.4.8—a widely used C library for parsing and creating
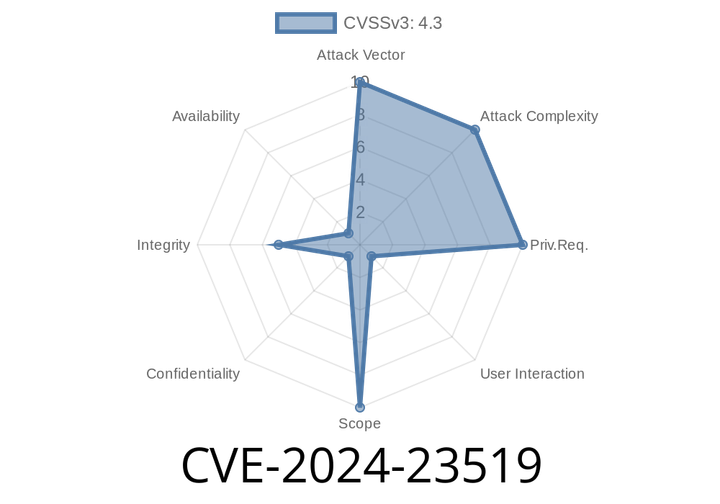
CVE-2024-23519 - Easy Exploit Guide for CSRF Vulnerability in M&S Consulting Email Before Download Plugin
---
If you run a WordPress website and use the “Email Before Download” plugin by M&S Consulting, you’ll want to hear about CVE-

CVE-2024-22251 - VMware Workstation and Fusion Out-of-Bounds Read in USB CCID (Chip Card Interface Device) – Explained in Simple Terms
A new vulnerability tagged CVE-2024-22251 has been discovered in VMware Workstation and VMware Fusion. This security risk comes from an out-of-bounds
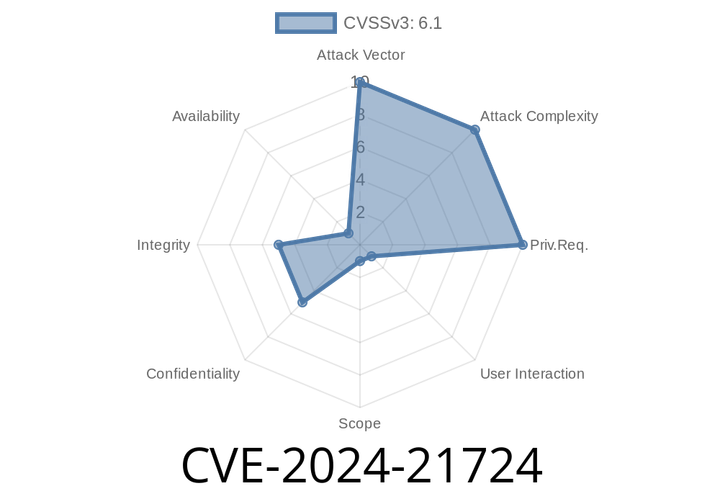
CVE-2024-21724 - Inadequate Input Validation in Media Selection Fields Leads to XSS Across Popular Extensions
In early 2024, security researchers uncovered a significant vulnerability — now tracked as CVE-2024-21724 — affecting a wide range of content management system (CMS) extensions
Episode
00:00:00
00:00:00