
CVE-2024-0604 - Critical Stored XSS Vulnerability in FooGallery WordPress Plugin (≤2.4.7) – Exclusive Analysis & Exploit Walkthrough
---
Introduction
WordPress sets the standard for website platforms, with plugins supercharging its functionality. But popularity also makes plugins a major attack vector. On January 2024,

CVE-2023-6247 - Crashing OpenVPN Clients — Inside the PKCS#7 Vulnerability
OpenVPN is one of the most trusted virtual private network (VPN) solutions out there. Many companies and users depend on it every day to protect
CVE-2023-50436 - Couchbase Server Admin Credentials Leaked in Logs – Full Analysis & Exploit Guide
In early 2024, security researchers uncovered a significant vulnerability in Couchbase Server (versions 7.1.5 up to but not including 7.2.4) identified
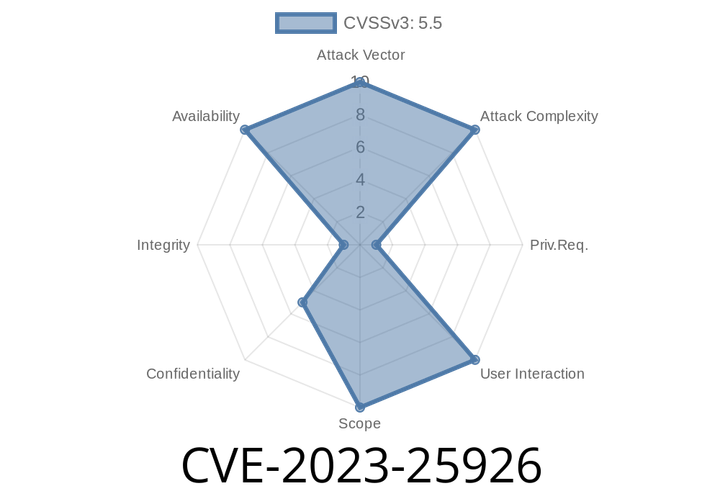
CVE-2023-25926 - Exploiting an XXE Flaw in IBM Security Guardium Key Lifecycle Manager (SKLM)
IBM Security Guardium Key Lifecycle Manager (SKLM) is a widely-used solution for enterprise key management, providing secure key generation, storage, and distribution for data-
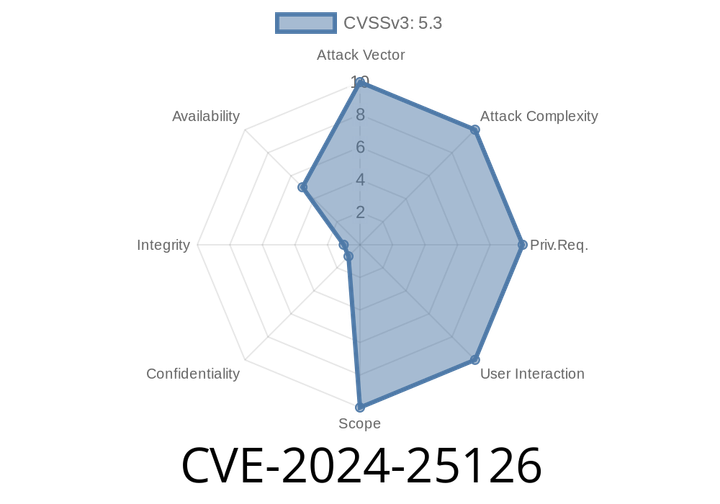
CVE-2024-25126 - How a Simple Header Can Take Down Your Ruby App (Rack Request Smuggling Explained)
In February 2024, a new security vulnerability hit the Ruby web world: CVE-2024-25126, affecting the widely used Rack library. Rack is a core
Episode
00:00:00
00:00:00