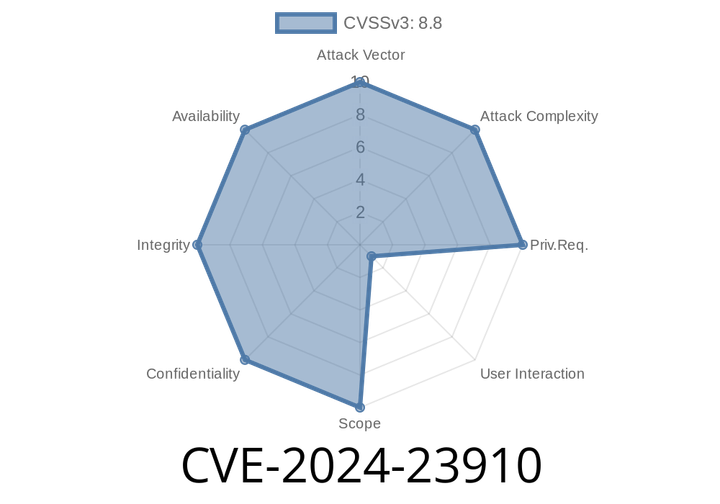
CVE-2024-23910 - Exploiting CSRF in ELECOM WiFi Routers and Repeaters – Real-World Impact & Exploit Details
In early 2024, a new cross-site request forgery (CSRF) vulnerability was disclosed in a range of ELECOM’s wireless LAN routers and repeaters, including

CVE-2024-21798 - Cross-Site Scripting (XSS) Vulnerability in ELECOM Wireless LAN Routers (WMC-X180GST-B and e-Mesh WMC-2LX-B) — Detailed Analysis and Exploit Walkthrough
ELECOM wireless LAN routers are widely used in homes and businesses across Japan and other parts of Asia. On February 13, 2024, JPCERT/CC disclosed

CVE-2024-25579 - OS Command Injection in ELECOM Routers (WMC-X180GST-B/e-Mesh Starter Kit) Explained
In early 2024, a critical OS command injection vulnerability was discovered in several ELECOM wireless LAN routers, most notably in the WMC-X180GST-B model,

CVE-2024-25422 - Breaking Down the SQL Injection Flaw in SEMCMS v4.8 (With Exploit Code & Detailed Walkthrough)
---
Summary
In early 2024, security researchers discovered a severe security flaw: CVE-2024-25422. This is a SQL Injection vulnerability present in the popular SEMCMS

CVE-2024-26559 - How a Simple Bug in uverif 2. Leaks Your Secrets
In February 2024, a concerning vulnerability shook the users of uverif v2. – a popular user verification tool adopted by several web platforms. The flaw – identified
Episode
00:00:00
00:00:00