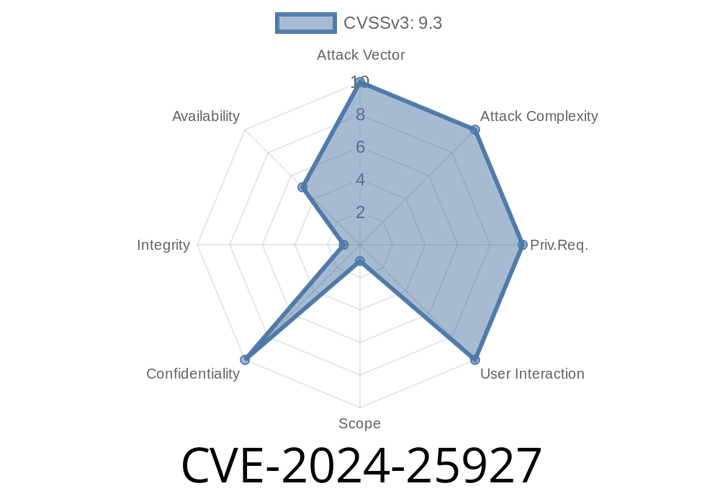
CVE-2024-25927 - SQL Injection in postMash – Custom Post Order (Joel Starnes) Explained
TL;DR:
CVE-2024-25927 is an SQL Injection vulnerability in the WordPress plugin "postMash – custom post order" by Joel Starnes. This flaw

CVE-2024-25910 - SQL Injection Vulnerability in Skymoonlabs MoveTo (Up to 6.2) – Exploit Details, Code Example, and Remediation
Summary:
A critical SQL Injection vulnerability (CVE-2024-25910) exists in Skymoonlabs MoveTo from unknown initial versions up through and including version 6.2. This

CVE-2024-24868 - SQL Injection Vulnerability in Smartypants SP Project & Document Manager (Through 4.69)
If you are managing files or projects using the Smartypants SP Project & Document Manager, you need to read this. A new critical vulnerability, CVE-

CVE-2024-25902 - Breaking Down the SQL Injection Vulnerability in miniorange Malware Scanner (Vulnerable up to 4.7.2)
In early 2024, a serious SQL Injection bug, tagged as CVE-2024-25902, was discovered in the popular miniorange Malware Scanner — a WordPress plugin known
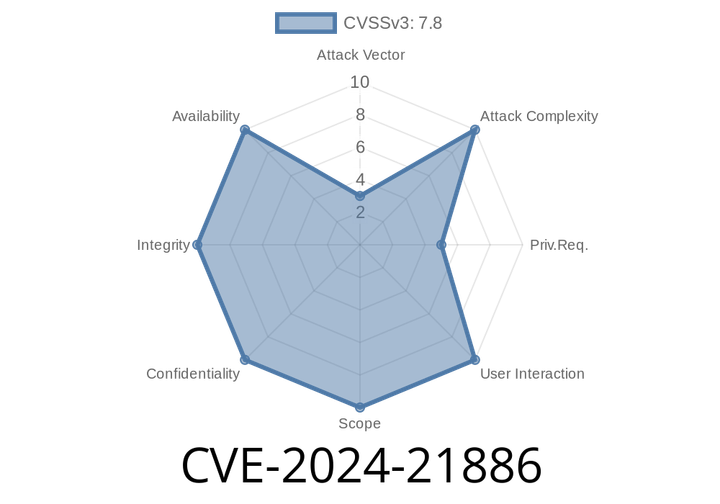
CVE-2024-21886 - Heap Buffer Overflow in X.Org Server’s DisableDevice Function Enables Remote Code Execution via SSH X11 Forwarding
In early 2024, security researchers uncovered a critical vulnerability affecting the X.Org Server, the backbone of graphical displays on many Unix-like operating systems.
Episode
00:00:00
00:00:00