
CVE-2024-1636 - Potential Cross-Site Scripting (XSS) in Page Editing Areas — Exclusive Deep Dive & Exploit Example
CVE-2024-1636 is a recently disclosed security vulnerability affecting the page editing interface in popular content management systems (CMS), including (but not limited to)

CVE-2024-1861 - Exploiting the Anti Hacker Scan Plugin Vulnerability in WordPress
The WordPress ecosystem is home to thousands of plugins. One such plugin — Disable Json API, Login Lockdown, XMLRPC, Pingback, Stop User Enumeration Anti Hacker Scan
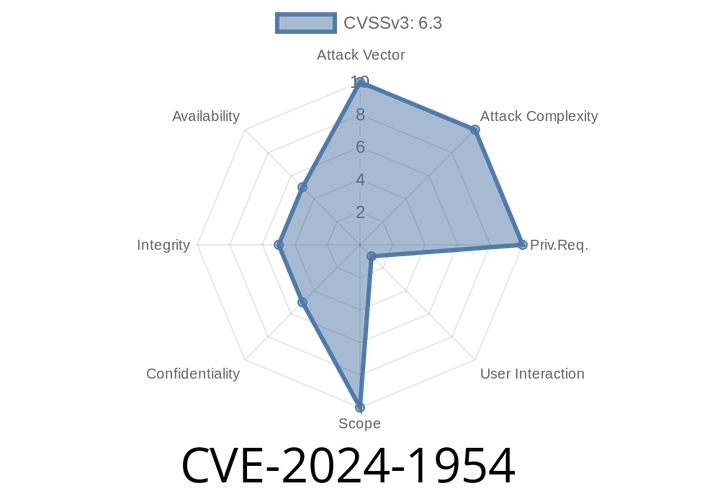
CVE-2024-1954 - Critical CSRF Vulnerability in Oliver POS - What You Need to Know and Exploitation Details
TL;DR:
A simple Cross-Site Request Forgery (CSRF) flaw in the Oliver POS WooCommerce plugin (up to version 2.4.1.8) allows remote

CVE-2024-22459 - Deep Dive—How a Simple Flaw in Dell ECS Exposed All Buckets to Attackers
Dell ECS is trusted worldwide as a robust object storage platform. But between versions 3.6 (up to 3.6.2.5), 3.7 (up

CVE-2024-1136 - How Attackers Bypass "Maintenance Mode" in Popular WordPress Plugin
Published: June 2024
Severity: Medium-High (CVSS: 6.5)
When a website goes under construction or needs a quick break, admins turn to plugins like
Episode
00:00:00
00:00:00