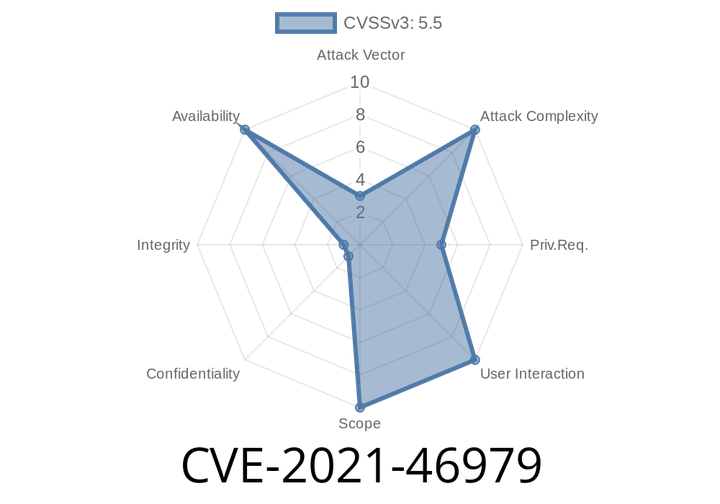
CVE-2021-46979 - Double Free Vulnerability in Linux Kernel IIO Core
In early 2021, a serious vulnerability was identified and fixed in the Linux kernel’s Industrial I/O (IIO) core subsystem. The flaw, tracked as

CVE-2024-27913 - How a malformed OSPF LSA packet Crashes FRRouting OSPF Daemon (Full Analysis & Exploit Walkthrough)
FRRouting (FRR) is one of the most widely used open-source routing suites, powering large portions of the internet and enterprise networks. In February 2024,

CVE-2023-50737 - Exploiting Lexmark Printer’s SE Menu to Run Arbitrary Code
Most home and office printers seem harmless, but what if your printer could be hacked and made to run unauthorized code? That’s the risk

CVE-2023-50736 - Memory Corruption Vulnerability in Lexmark PostScript Interpreter Exploited
In late 2023, a serious security flaw — CVE-2023-50736 — was disclosed, affecting the PostScript interpreter in a range of Lexmark printers and multifunction devices.
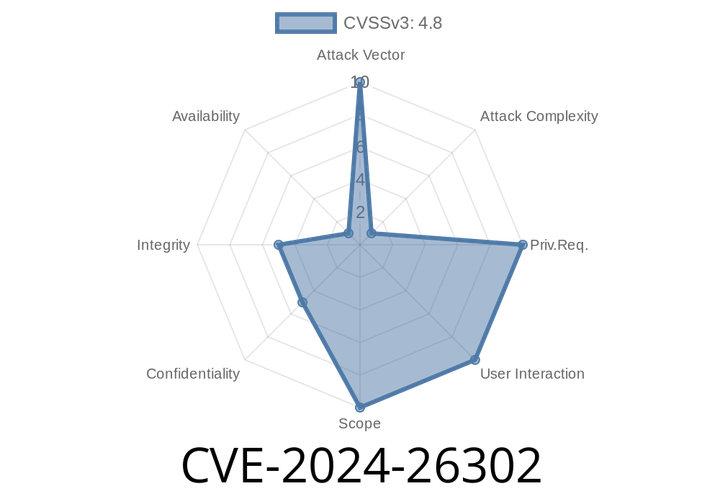
CVE-2024-26302 - Exploiting Sensitive Information Disclosure in ClearPass Policy Manager’s Web Interface
In February 2024, Aruba Networks disclosed a vulnerability tracked as CVE-2024-26302 affecting their widely used ClearPass Policy Manager. This vulnerability, rated as “medium”
Episode
00:00:00
00:00:00