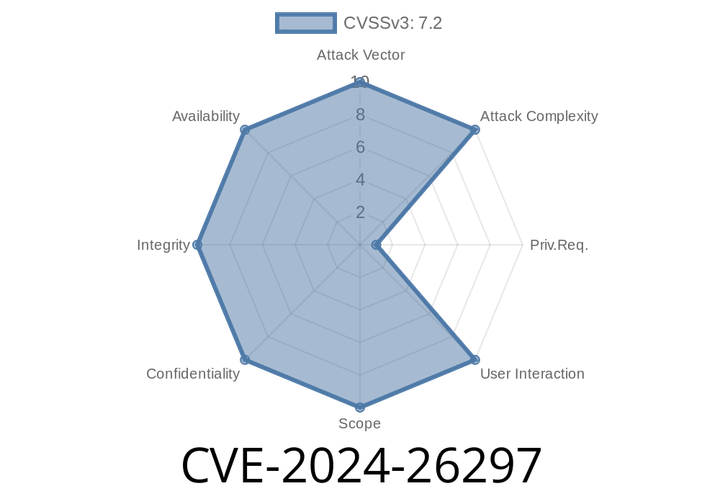
CVE-2024-26297 - Exploiting Critical Remote Command Execution in HPE ClearPass Policy Manager
CVE-2024-26297 is a newly disclosed critical vulnerability affecting the HPE Aruba ClearPass Policy Manager. If you run a ClearPass web management interface in

CVE-2024-0763 - How Bad Folder Sanitization Lets Authenticated Users Delete Any Folder on Your Server
Summary:
CVE-2024-0763 is a serious vulnerability that allows any authenticated user to delete any folder (including all its contents) on a remote server.

CVE-2024-24027 - SQL Injection in Likeshop Before 2.5.7—How It Works, Exploit Details, and How to Protect Yourself
CVE-2024-24027 is a major security concern for anyone running the Likeshop e-commerce platform before version 2.5.7. This vulnerability allows attackers
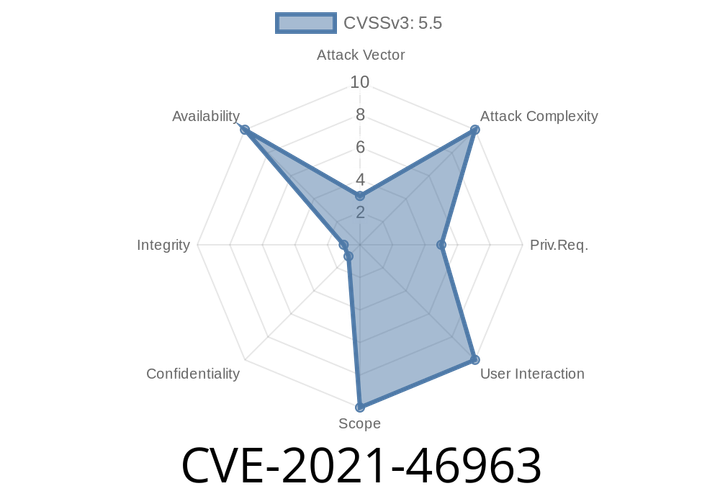
CVE-2021-46963 - Deep Dive Into the qla2xxx_mqueuecommand() Crash in the Linux Kernel
Linux powers the majority of today's servers. Its reliability and security are crucial for everything from web hosting to scientific computing. Kernel drivers,
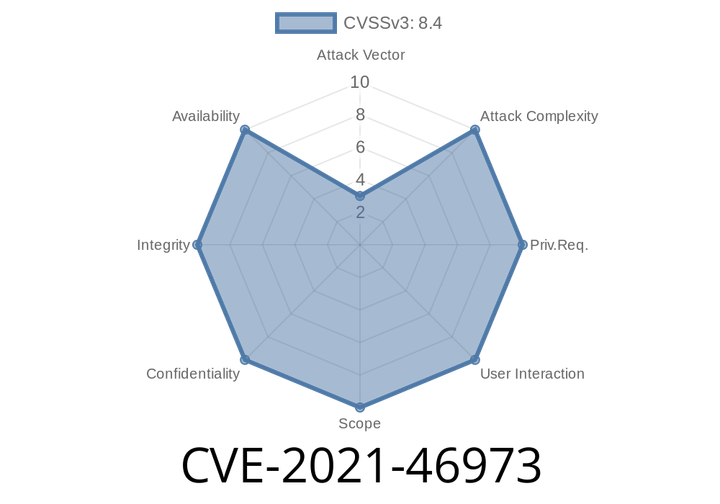
CVE-2021-46973 - Understanding and Exploiting Use-After-Free in Linux Kernel QRTR MHI Transmission
In early 2021, researchers and Linux kernel developers identified and patched a serious vulnerability (now tracked as CVE-2021-46973) in the Linux kernel'
Episode
00:00:00
00:00:00