CVE-2021-46946 - Understand Why This Vulnerability Was Rejected
When you’re hunting for cybersecurity CVEs (Common Vulnerabilities and Exposures), sometimes you’ll bump into IDs like CVE-2021-46946 and wonder what dangerous

CVE-2024-25843 - How a Guest Could Hack PrestaShop Sites via "Import/Update Bulk Product from any Csv/Excel File Pro" Module
PrestaShop is a popular e-commerce platform used worldwide. Add-ons enhance its abilities, but sometimes they also introduce security risks. This is the case

CVE-2024-24323 - SQL Injection in Linlinjava Litemall v1.8. — Deep Dive, Exploit and How to Patch
CVE-2024-24323 is a critical SQL injection vulnerability discovered in Linlinjava Litemall v1.8., an open-source e-commerce platform growing in popularity for
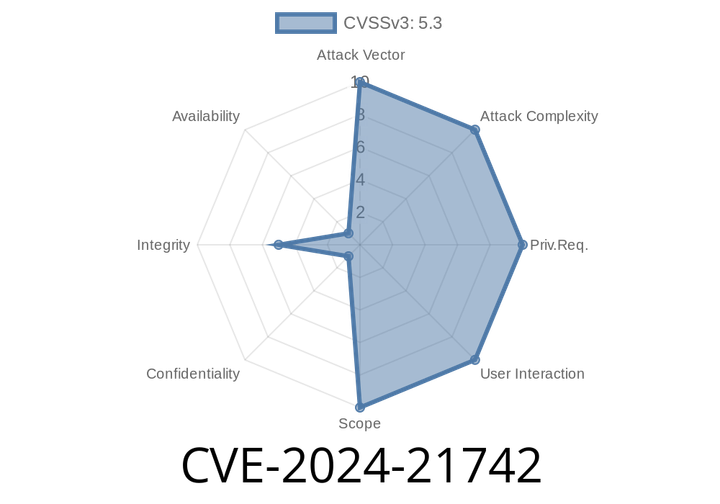
CVE-2024-21742 - Header Injection in Apache James MIME4J DOM Explained
In June 2024, a security vulnerability was identified in the Apache James MIME4J library, registered as CVE-2024-21742. This flaw arises from improper input
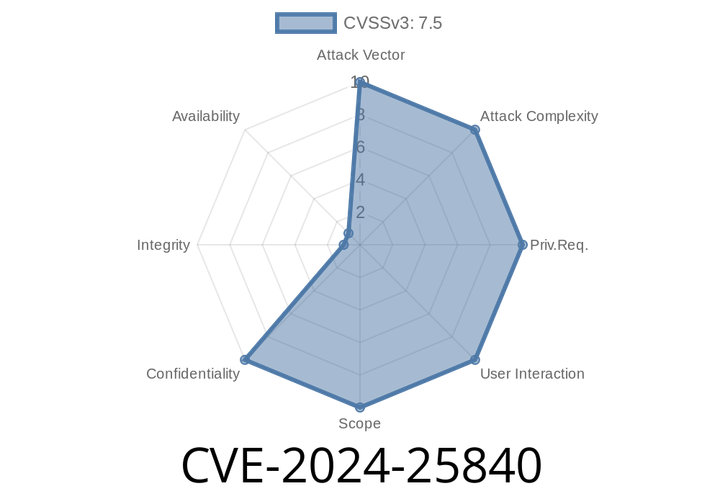
CVE-2024-25840 - Path Traversal in PrestaSalesManager lets Guests Download Personal Info in PrestaShop
Published: June, 2024
Impacts: Presta World "Account Manager | Sales Representative & Dealers | CRM" (prestasalesmanager) module versions up to 9.
Environment: PrestaShop e-commerce
Episode
00:00:00
00:00:00