
CVE-2024-25400 - Subrion CMS 4.2.1 SQL Injection in ia.core.mysqli.php — What’s Really Going On?
In early 2024, a security advisory caught the web application world’s attention: Subrion CMS 4.2.1 allegedly contained a serious SQL Injection vulnerability

CVE-2024-1403 - Authentication Bypass in Progress OpenEdge – Explained, Exploited, and Secured
A critical security vulnerability—CVE-2024-1403—has been discovered in the Progress OpenEdge Authentication Gateway and AdminServer. If you’re running OpenEdge versions prior
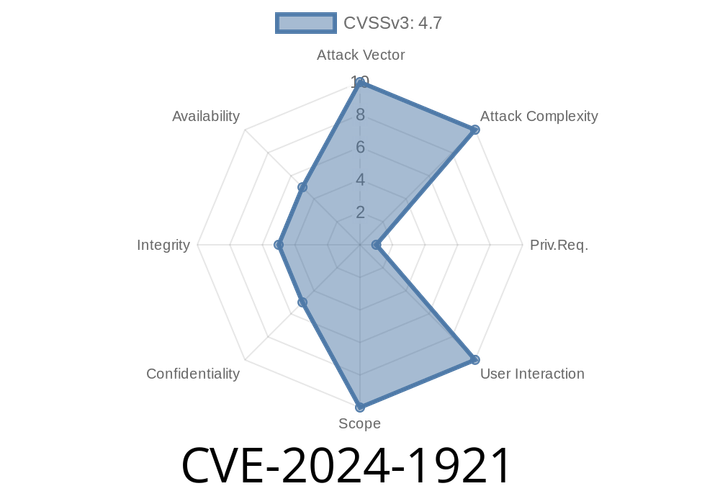
CVE-2024-1921 - Critical Unrestricted File Upload Vulnerability in osuuu LightPicture – Exploit, Details, and Mitigation
On March 26, 2024, a critical vulnerability identified as CVE-2024-1921 (also tracked as VDB-254856) was discovered in the *osuuu LightPicture* image management

CVE-2024-25723 - How a ZenML API Flaw Led to Remote Privilege Escalation (Exploit Walkthrough & Fix Details)
ZenML has quickly become a popular tool for machine learning pipelines, but security sometimes takes a backseat in fast-moving open source projects. CVE-2024-
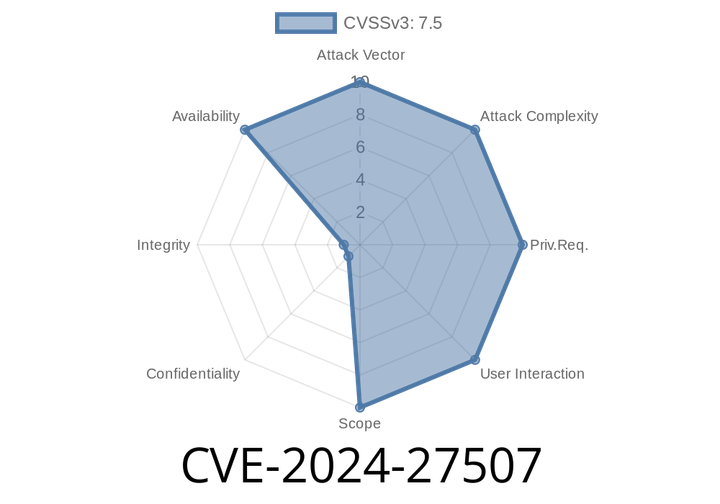
CVE-2024-27507 - Memory Leak Vulnerability in libLAS 1.8.1 (ts2las.cpp) — Deep Dive and Exploit Example
A serious memory leak has been identified in the LAS tools library, libLAS version 1.8.1, specifically in the /libLAS/apps/ts2las.cpp source
Episode
00:00:00
00:00:00