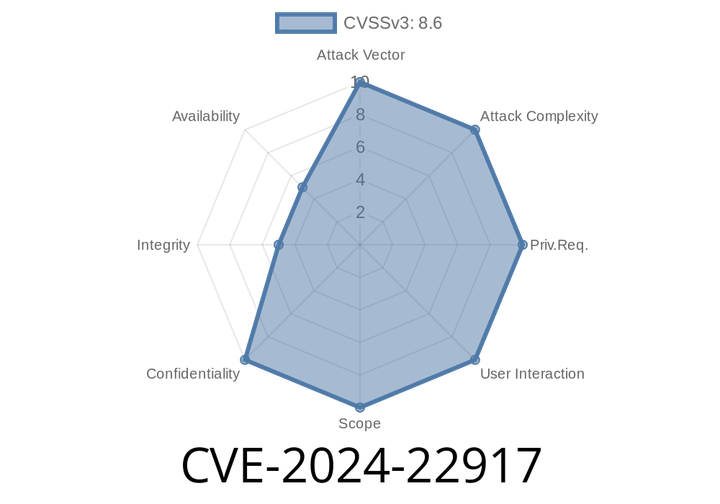
CVE-2024-22917 - Critical SQL Injection in Dynamic Lab Management System Project v1. (PHP) – Explained with Code, Exploit, and Fix
Date disclosed: June 2024
Vulnerability type: SQL Injection (Remote Code Execution)
Project affected: Dynamic Lab Management System Project v1. (PHP)
CVSS Score: 9.8 (Critical)

CVE-2024-22544 - Critical RCE in Linksys E170 Routers Via the setDateTime Function (Exploit Walkthrough & Code Samples)
In early 2024, security researchers uncovered a serious flaw in the Linksys E170 router, version 1..04 (build 3). This vulnerability, tracked as CVE-2024-
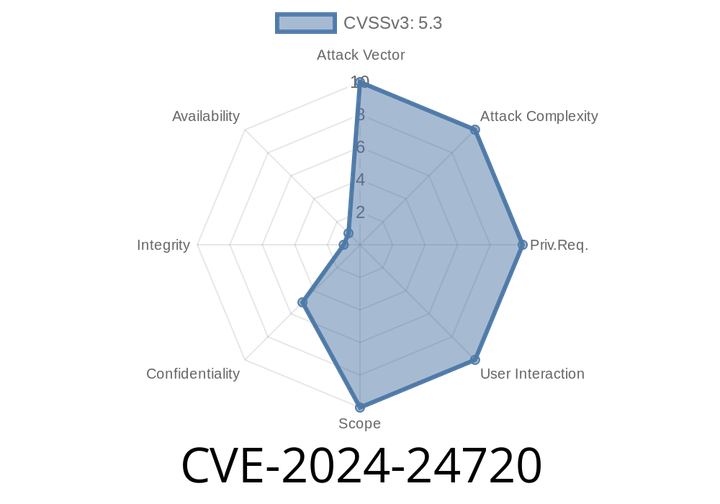
CVE-2024-24720 - How Innovaphone PBX Forgot-Password Leaks User Existence (Explained with Code and Examples)
A recently discovered security flaw, CVE-2024-24720, affects Innovaphone PBX appliances (before version 14r1). The vulnerability is surprisingly simple—but still quite dangerous. Here’

CVE-2024-22543 - Escalating Privileges on Linksys E170 Routers – A Deep Dive and Exploit Example
---
Overview
A newly identified vulnerability, CVE-2024-22543, affects the popular Linksys Router E170 (version 1..04, build 3). This flaw allows an attacker, who
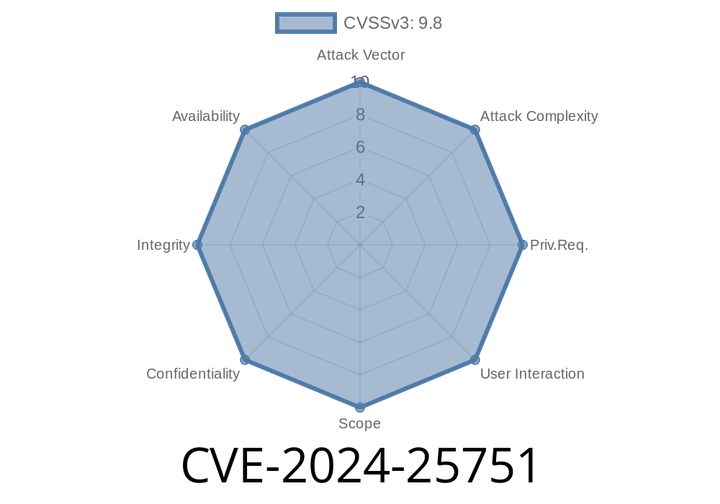
CVE-2024-25751 - Remote Code Execution in Tenda AC9 (v3., Firmware v15.03.06.42_multi) via Stack-Based Buffer Overflow
The Tenda AC9 wireless router is a popular home networking device. However, a severe vulnerability—CVE-2024-25751—was discovered in its firmware (version 15.
Episode
00:00:00
00:00:00