
CVE-2024-26604 - How a Linux Kernel Kobject Check Went Wrong – Exploit Details and Patch Review
In February 2024, a confusing bug struck the heart of the Linux kernel. Identified as CVE-2024-26604, it all circles around the humble kobject

CVE-2024-26465 - Critical DOM-based XSS in stewdio beep.js (Before commit ef22ad7) Explained with Exploit Details
CVE-2024-26465 is a DOM-based Cross-Site Scripting (XSS) vulnerability detected in the /beep/Beep.Instrument.js component of stewdio beep.js, a

CVE-2024-26468 - DOM-based XSS in jstrieb/urlpages index.html (Full Analysis, Code & Exploit Example)
CVE-2024-26468 uncovers a DOM-based Cross-Site Scripting (XSS) in the index.html component of jstrieb/urlpages before commit 035b647. This high-severity
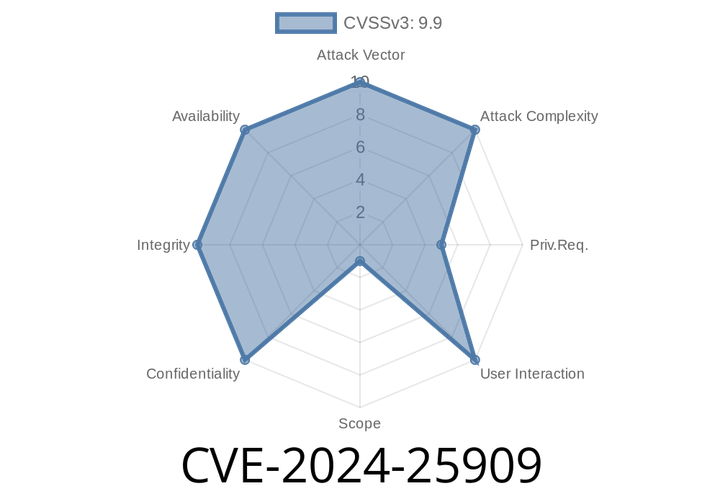
CVE-2024-25909 - Unrestricted Upload of Dangerous Files in JoomUnited WP Media Folder (WP Media Folder ≤ 5.7.2)
On February 2024, a critical vulnerability identified as CVE-2024-25909 made headlines for impacting the popular WordPress plugin WP Media Folder (developed by JoomUnited)

CVE-2024-25763 - openNDS 10.2. Use-After-Free Vulnerability Exploited
TL;DR:
openNDS 10.2., a popular open-source Captive Portal solution used on OpenWrt routers, contains a serious Use-After-Free (UAF) vulnerability in
Episode
00:00:00
00:00:00