
CVE-2024-25850 - Command Injection in Netis WF278 v2.1.40144 via wps_ap_ssid5g Parameter
Table of Contents
Introduction
Home and small-business routers are prime targets for cyber attackers, largely because they often lack basic security. Netis WF278, a
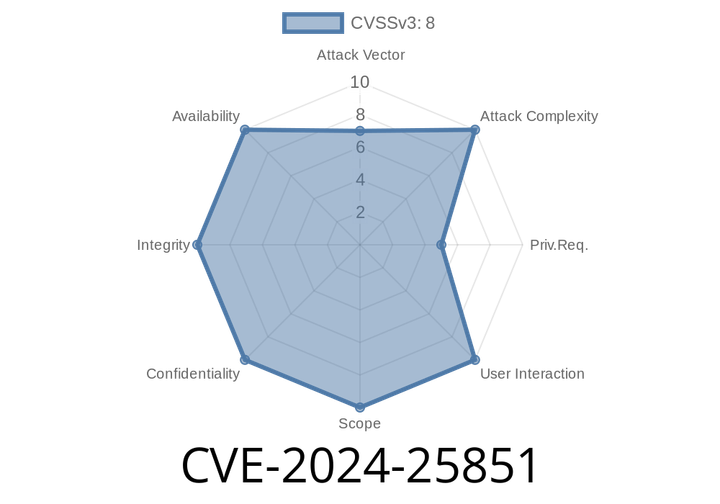
CVE-2024-25851 - Command Injection in Netis WF278 v2.1.40144 via cgitest.cgi (config_sequence)
In early 2024, a critical vulnerability—CVE-2024-25851—was found in the Netis WF278 wireless router, version v2.1.40144. This issue makes it

CVE-2024-26284 - Exploiting UXSS in Focus for iOS (< 123) with a 302 Redirect
On February 2024, a serious vulnerability — CVE-2024-26284 — was disclosed in Focus for iOS, a popular content blocker. This bug allows attackers to perform

CVE-2024-25876 - XSS Vulnerability in Enhavo CMS v.13.1 Header Module – Exploit Details and Mitigation
Enhavo CMS is a flexible content management system built with Symfony and Open Source for building websites fast and efficiently. Recently, a security vulnerability has
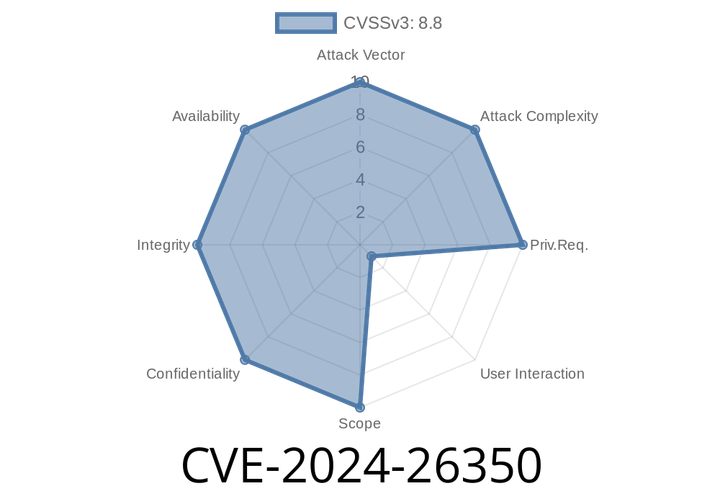
CVE-2024-26350 - Exploiting CSRF in flusity-CMS v2.33 via /core/tools/update_contact_form_settings.php
---
Flusity-CMS is a popular open-source content management system favored for its lightweight structure and customization options. However, in early 2024, security researchers found
Episode
00:00:00
00:00:00