CVE-2024-23131 - Memory Corruption in Autodesk DLLs via Malicious STP File – Detailed Breakdown and Exploit Insights
The design and architecture industries rely heavily on Autodesk applications for handling 3D data, such as drawings and models shared through the STP or STEP
CVE-2024-23132 - Deep Dive into a Dangerous AutoCAD Memory Corruption Flaw and How It’s Exploited
In early 2024, cybersecurity researchers discovered a critical flaw in Autodesk AutoCAD, tracked as CVE-2024-23132. This vulnerability, lurking in the way AutoCAD’s
CVE-2024-23128 - Memory Corruption in Autodesk via Malicious MODEL Files – Technical Deep Dive & Exploitation
CVE-2024-23128 is a critical vulnerability affecting multiple Autodesk applications. At its heart is a memory corruption issue, specifically a write access violation, that
CVE-2024-23129 - Memory Corruption in opennurbs.dll via Crafted 3DM, STP, or SLDASM Files – Exploit Details and Analysis
---
Summary:
CVE-2024-23129 is a serious vulnerability that affects multiple Autodesk applications due to unsafe parsing of 3D model files like 3DM, STP, or
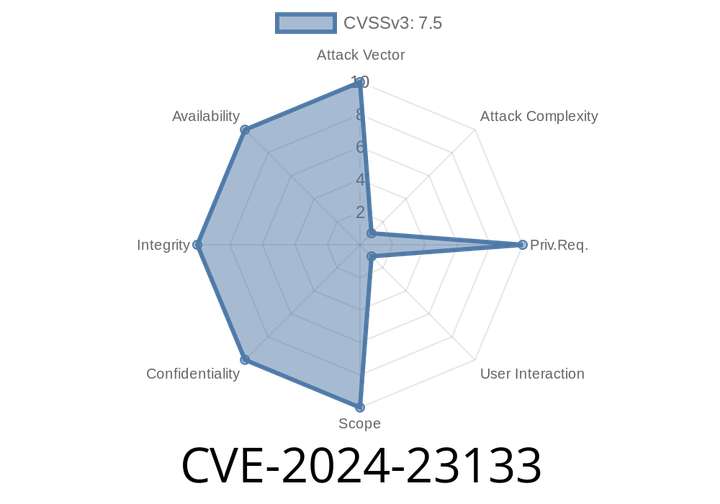
CVE-2024-23133 - Memory Corruption and Code Execution with Malicious STP File in Autodesk AutoCAD (ASMDATAX228A.dll)
CVE-2024-23133 is a newly disclosed vulnerability affecting Autodesk AutoCAD, specifically the way it handles STP (STEP) files via the ASMDATAX228A.dll component. If
Episode
00:00:00
00:00:00