
CVE-2024-25288 - SQL Injection in SLIMS 9 Bulian v9.6.1 (pop-scope-vocabolary.php) – How the Exploit Works
If you’re running an online library with SLIMS (Senayan Library Management System), you should really pay attention to a recently disclosed vulnerability: CVE-2024-

CVE-2024-22220 - Breaking Down the Unauthenticated Stored XSS in Terminalfour and Formbank
---
Introduction
CVE-2024-22220 is a critical vulnerability discovered in *Terminalfour* (versions 7.4 through 7.4.0004 QP3, 8 through 8.3.19) and
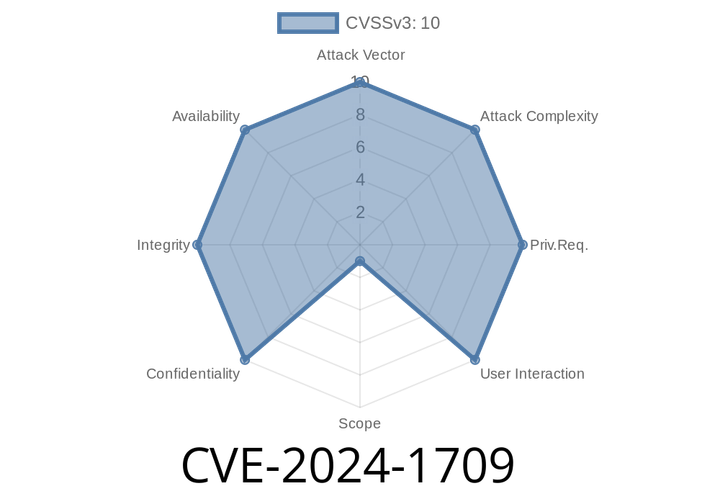
CVE-2024-1709 - How Hackers Bypass Authentication in ConnectWise ScreenConnect (23.9.7 and Below)—Deep Dive & Exploit Guide
ConnectWise ScreenConnect is widely used by IT helpdesks and MSPs for remote desktop and server management. Unfortunately, a major vulnerability—CVE-2024-1709—was recently

CVE-2023-49100 - Trusted Firmware-A (TF-A) SDEI Service Out-of-Bounds Read Exploit Explained
Published: June 2024
Introduction
In late 2023, a vulnerability labeled CVE-2023-49100 was found in Trusted Firmware-A (TF-A), a critical project powering

CVE-2022-45169 - Stealing Clicks with Open Redirect & Push Notification Exploit in LIVEBOX vDesk
In late 2022, security researchers discovered a surprisingly simple but dangerous flaw in the popular enterprise software, LIVEBOX Collaboration vDesk (up to version v031). This
Episode
00:00:00
00:00:00