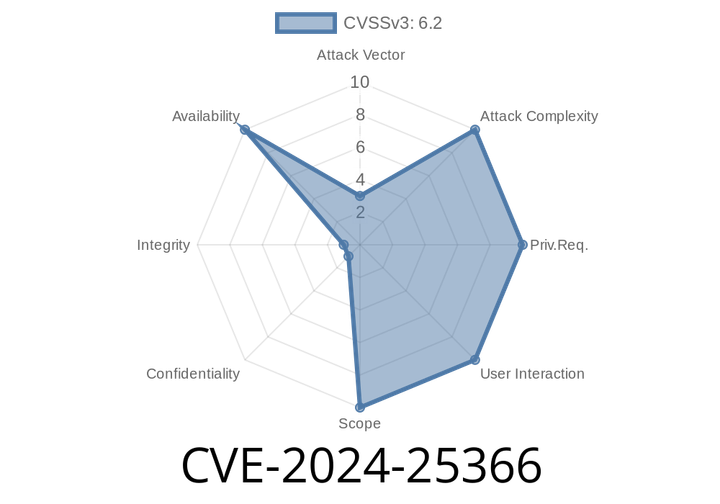
CVE-2024-25366 - Buffer Overflow in mz-automation.de libiec61850 v.1.4. — Full Details and Exploit Explained
Date: June 2024
Vulnerability Type: Buffer Overflow
CVSS Score: 8.6 (High)
Product: mz-automation.de libiec61850 v.1.4.
Component: mms_getnamelist_service (mmsServer_
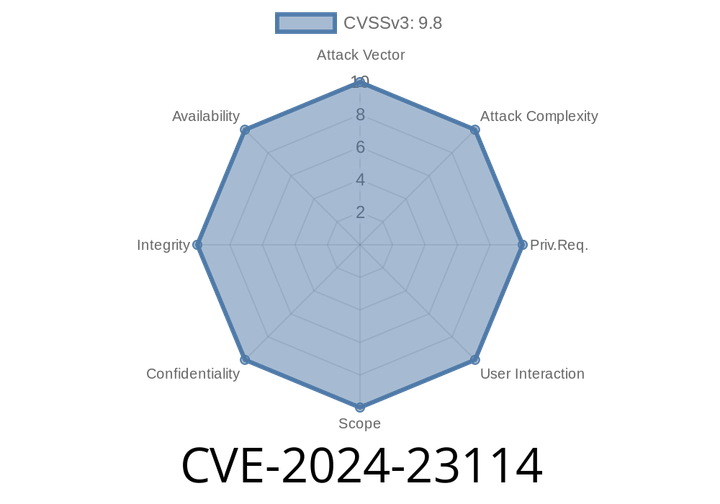
CVE-2024-23114 - Understanding the Apache Camel CassandraQL AggregationRepository Unsafe Deserialization Flaw
A serious vulnerability—CVE-2024-23114—was discovered in Apache Camel's CassandraQL AggregationRepository component. This flaw exposes applications to unsafe deserialization attacks whenever
CVE-2024-22369 - Deserialization of Untrusted Data in Apache Camel SQL Component — Full Analysis & Exploit Example
CVE-2024-22369 uncovers a serious vulnerability in the Apache Camel SQL component resulting from unsafe deserialization of untrusted data. This flaw affects critical Apache
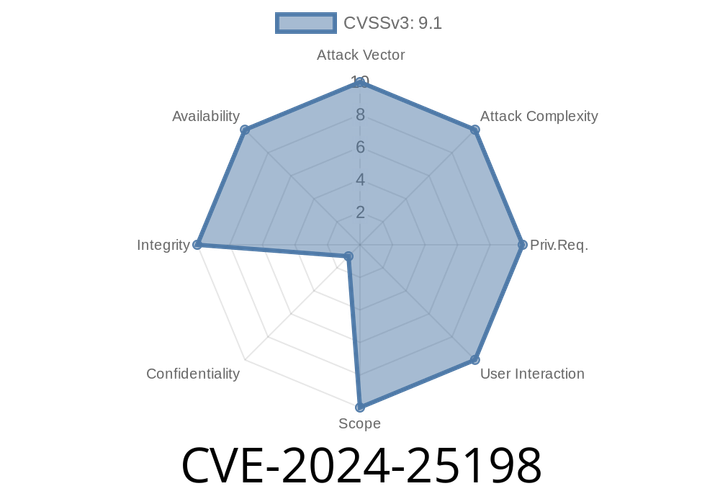
CVE-2024-25198 - Use-After-Free Exploit in ROS2 Nav2 (humble) via Incorrect Pointer Reset Order in amcl_node.cpp
A critical vulnerability, CVE-2024-25198, was recently identified in the Open Robotics Robotic Operating System 2 (ROS2), specifically in the Nav2 package, humble version.

CVE-2024-1557 - Memory Safety Bugs in Firefox 122 - What You Need to Know
Published: June 2024
Severity: High
Affected Versions: Firefox < 123 (including Firefox 122)
Attack Vector: Remote
Exploitability: Possible Arbitrary Code Execution
Introduction
A new critical
Episode
00:00:00
00:00:00