
CVE-2024-1547 - How Attackers Exploited Alert Dialogs in Firefox to Fool Users
In February 2024, Mozilla fixed an intriguing vulnerability: CVE-2024-1547. If you used Firefox, Firefox ESR, or Thunderbird before their February 2024 updates, your
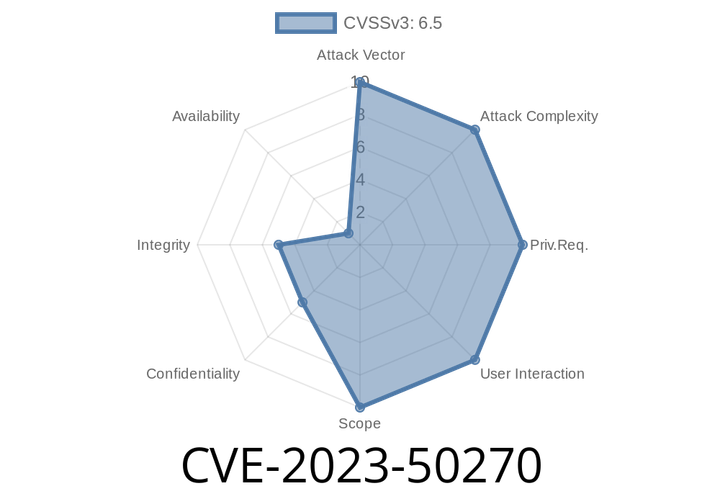
CVE-2023-50270 - Session Fixation in Apache DolphinScheduler Before 3.2. Explained (With Exploit Example)
Apache DolphinScheduler is a popular big data workflow orchestrator, used by many organizations for automating complex data processes. However, a critical security vulnerability has been
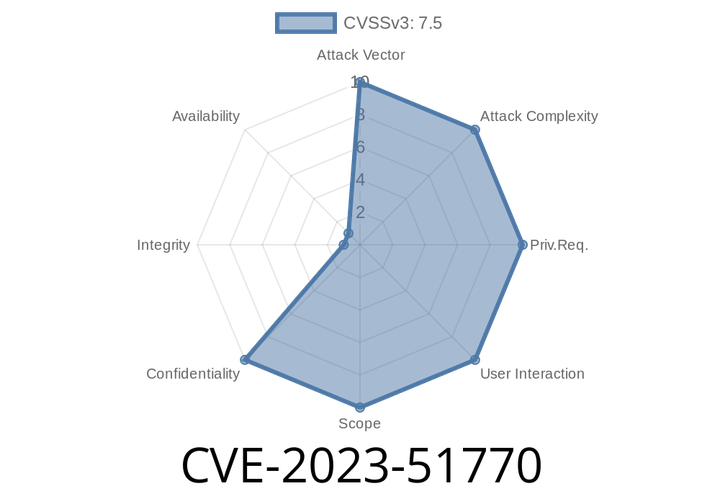
CVE-2023-51770 - Arbitrary File Read Vulnerability in Apache DolphinScheduler (before 3.2.1) – Explained With Exploit & Code!
---
Introduction
A new security issue, CVE-2023-51770, was discovered in Apache DolphinScheduler (versions before 3.2.1). This vulnerability lets attackers read *any file*
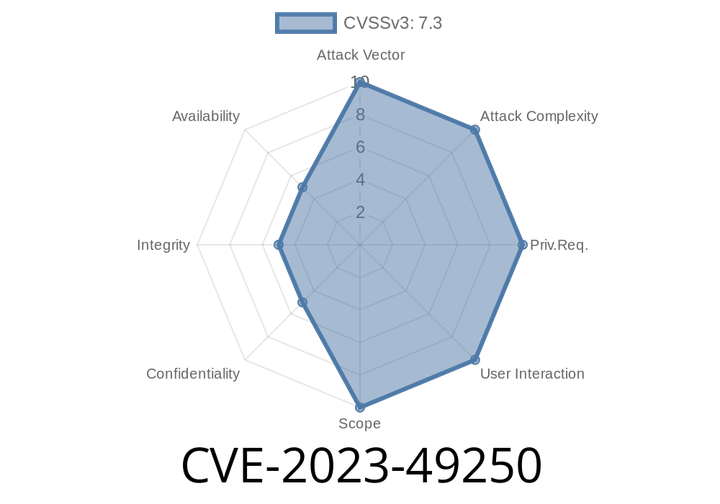
CVE-2023-49250 - DolphinScheduler’s Insecure HTTPS Handling – How a MITM Can Spoof Your Server
Apache DolphinScheduler is a powerful open-source workflow scheduler system, widely used for orchestrating complex data pipelines. But recently, a critical security flaw was found
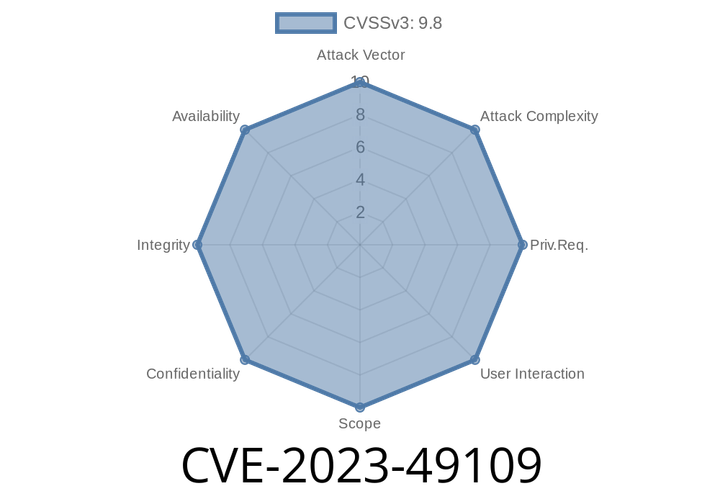
CVE-2023-49109 - How Remote Code Execution Haunted Apache DolphinScheduler (with Exploit Details)
---
Apache DolphinScheduler is a popular open-source platform for orchestrating data pipelines. But in late 2023, cyber researchers discovered a serious vulnerability—CVE-2023-49109—
Episode
00:00:00
00:00:00