
CVE-2024-25974 - Stored XSS in OpenOlat LMS’s Media Center Exposes All Users
A critical security flaw—CVE-2024-25974—has been discovered in Frentix GmbH’s popular OpenOlat Learning Management System (LMS). The vulnerability allows an authenticated
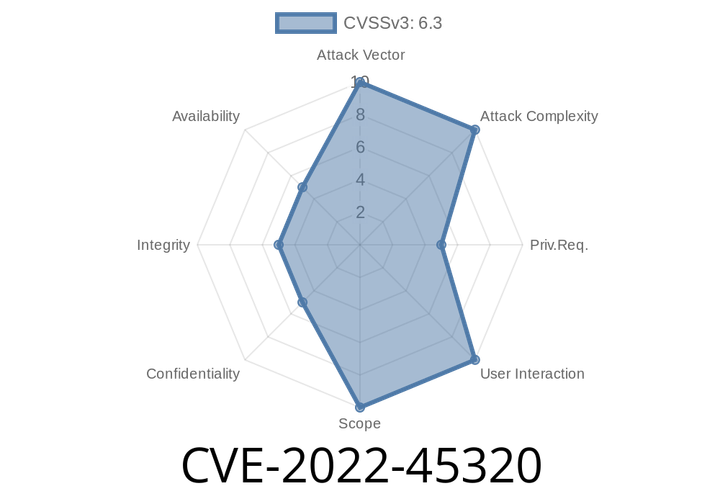
CVE-2022-45320 - Remote Wiki Page Takeover in Liferay Portal Explained
Liferay is a popular open-source portal used by businesses worldwide to build web platforms. But just like any software, it isn't immune
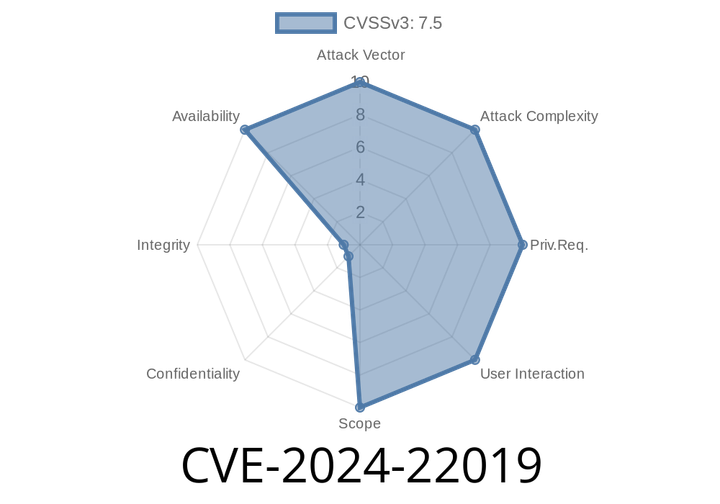
CVE-2024-22019 - Exploiting Node.js Chunked Encoding to Exhaust Server Resources
In early 2024, a serious vulnerability—CVE-2024-22019—was discovered affecting the core of Node.js HTTP servers. By sending a maliciously crafted HTTP
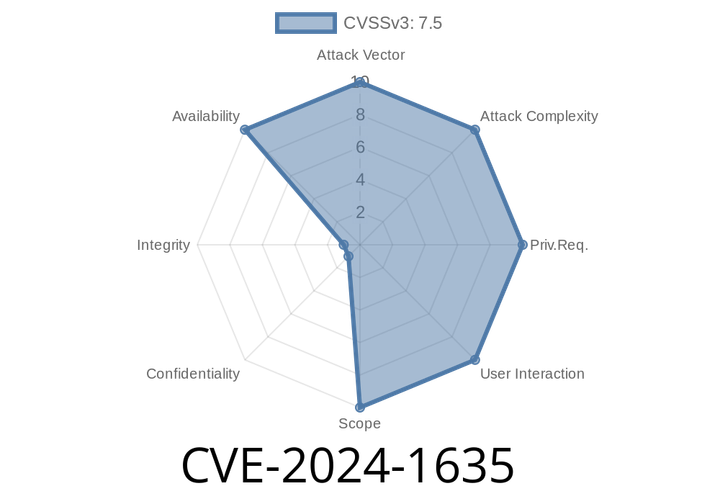
CVE-2024-1635 - A Deep Dive into Undertow’s HTTP Upgrade Memory Leak (WildFly-HTTP-Client)
A recent critical vulnerability — CVE-2024-1635 — has been identified in Undertow, a prominent web server widely used in Java enterprise stacks. This flaw specifically

CVE-2024-26308 - Resource Exhaustion Vulnerability in Apache Commons Compress (Versions 1.21–1.25) Explained
On February 27, 2024, Apache disclosed CVE-2024-26308, a serious vulnerability in the popular Apache Commons Compress library. This vulnerability concerns "Allocation of
Episode
00:00:00
00:00:00