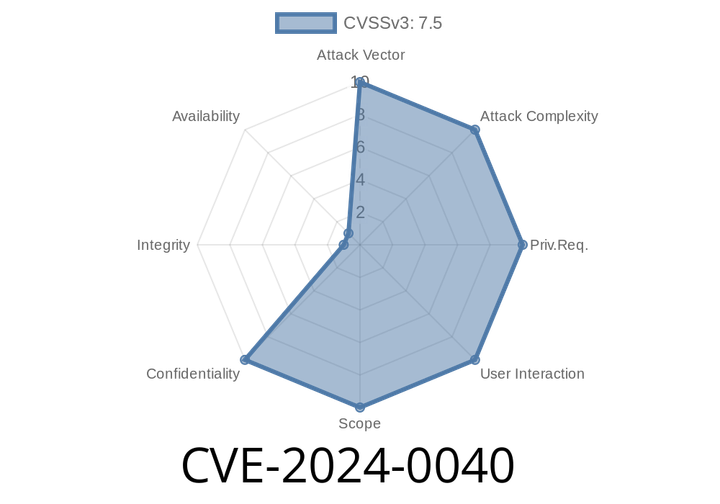
CVE-2024-0040: Uncovering a Potential Heap Buffer Overflow Vulnerability in setParameter of MtpPacket.cpp
---
Introduction
We have recently discovered a concerning vulnerability in the MtpPacket.cpp code that appears as a possible out of bounds read due to a

CVE-2024-0036 - **How a Logic Flaw in Android’s ActivityTaskManagerService Lets Apps Bypass Activity Start Restrictions
In January 2024, a significant vulnerability—CVE-2024-0036—was discovered in the Android Open Source Project (AOSP). The bug is rooted in the startNextMatchingActivity

CVE-2024-0035 - Exploiting the onNullBinding Vulnerability in TileLifecycleManager.java for Local Privilege Escalation
In early 2024, security researchers uncovered a critical Android vulnerability: CVE-2024-0035. This flaw lies in the onNullBinding method of the TileLifecycleManager.java file,

CVE-2024-0014 - Logic Error in `UpdateFetcher.java` Allows Local Privilege Escalation (With Code Example & Exploit Details)
---
A new vulnerability, CVE-2024-0014, has been discovered in the Android system's update process, specifically in the UpdateFetcher.java file. This bug

CVE-2024-0030: Exploring an Out of Bounds Read in btif_to_bta_response of btif_gatt_util.cc
In the world of cybersecurity, understanding and mitigating vulnerabilities is crucial to keep systems and devices secure. In this long-read post, we will investigate
Episode
00:00:00
00:00:00