
CVE-2023-6536 - Exploiting NULL Pointer Dereference in Linux NVMe/TCP Driver - Step-by-Step Analysis and Exploit Example
In December 2023, security researchers discovered and published details about CVE-2023-6536, a critical vulnerability found in the Linux kernel's NVMe driver.
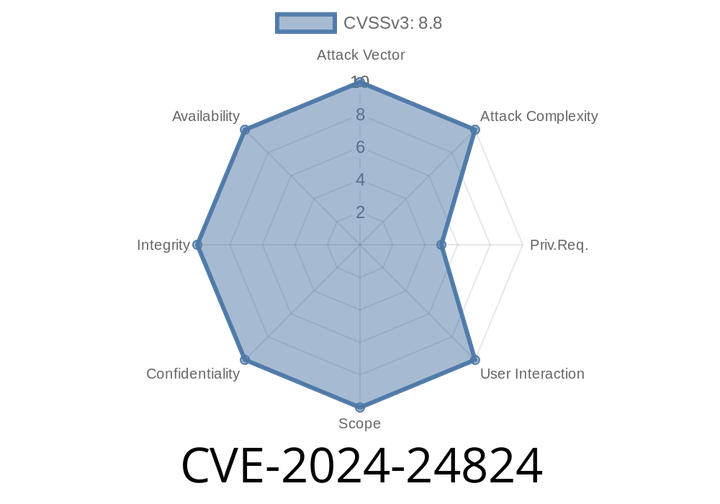
CVE-2024-24824 - Exploiting Arbitrary Class Loading in Graylog (Full Walkthrough)
CVE-2024-24824 is a critical security vulnerability affecting Graylog versions starting from 2.. up to but not including 5.1.11 and 5.2.

CVE-2024-24823 - Session Hijacking Vulnerability in Graylog – Exploit Details & Remediation
CVE-2024-24823 is a recently disclosed security vulnerability affecting Graylog, a widely used free and open source log management platform. The issue exists in
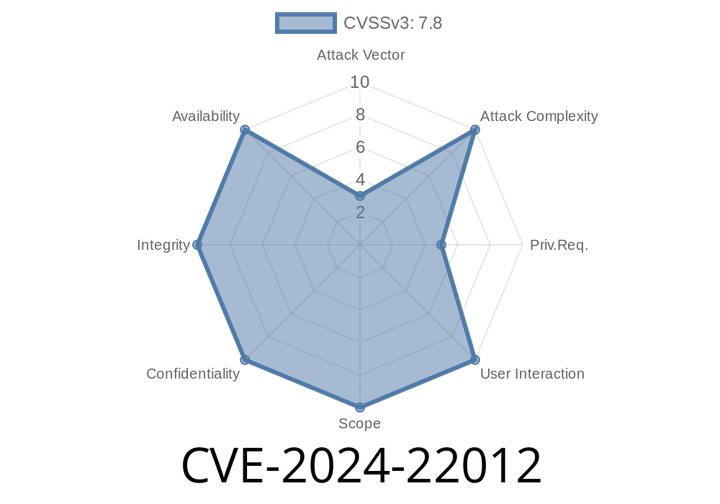
CVE-2024-22012 - Out-of-Bounds Write Lets Local Users Escalate Privileges—Explained
A new vulnerability tracked as CVE-2024-22012 has been making headlines in the security community. This issue, caused by a missing bounds check, can
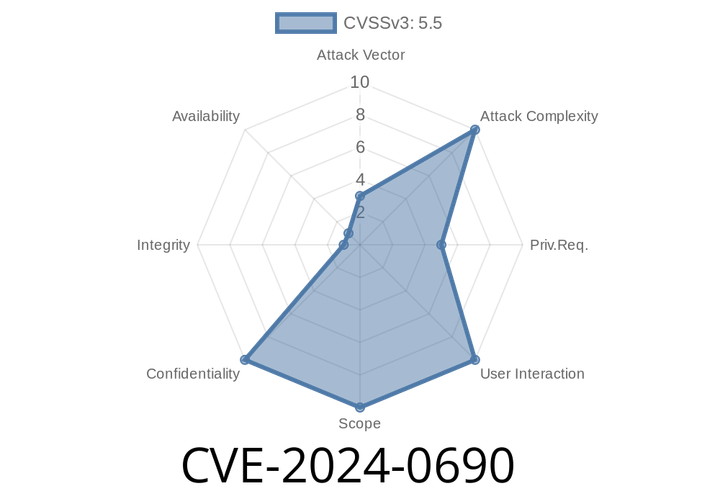
CVE-2024-0690 - Information Disclosure via ANSIBLE_NO_LOG Misconfiguration in Ansible-Core
Recently, a new security vulnerability was discovered in ansible-core, designated as CVE-2024-0690, which affects a wide range of systems. The vulnerability is
Episode
00:00:00
00:00:00