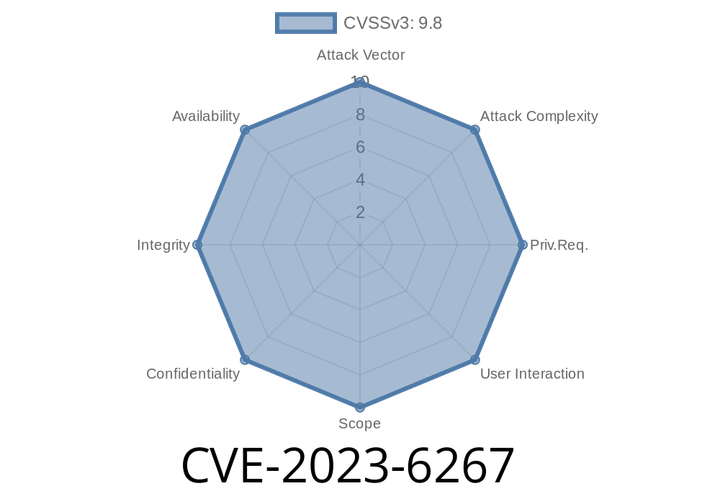
CVE-2023-6267 - How a JSON Payload Flaw Bypasses Annotation-Based Security in REST APIs
In December 2023, a critical vulnerability (designated as CVE-2023-6267) was discovered affecting systems that use annotation-based security for REST APIs, particularly when

CVE-2023-40547 - Remote Code Execution in Shim Bootloader – Exploit Explained
On August 14, 2023, a critical vulnerability (CVE-2023-40547) was publicly reported in the Shim bootloader. Shim is a critical component in many Linux
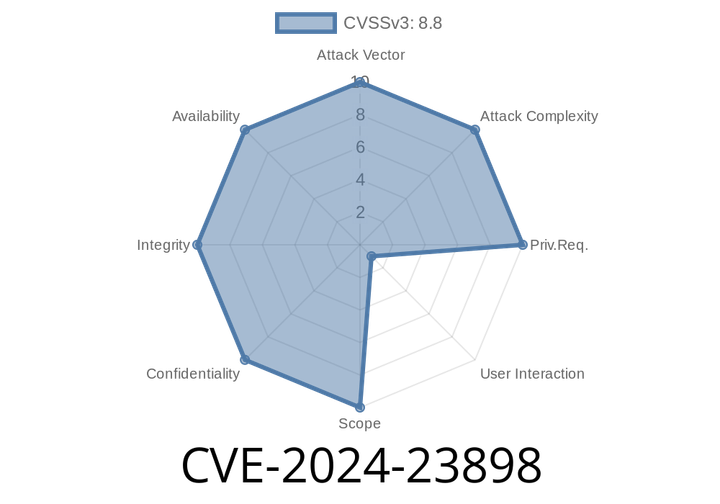
CVE-2024-23898 - Breaking Jenkins Security – A Deep Dive into Critical CSWSH Vulnerability (with Exploit Details)
Jenkins is one of the most popular automation servers out there. Hundreds of thousands of companies rely on it to build, test, and ship their
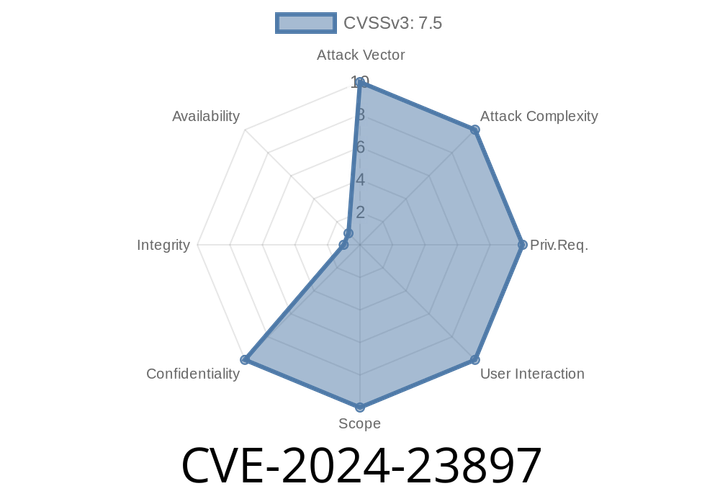
CVE-2024-23897 - Inside the Jenkins CLI Exploit That Lets Attackers Read Files - A Deep Dive
Jenkins is a very popular open-source automation server used in countless development and deployment pipelines worldwide. Like all powerful tools, Jenkins sometimes carries risks,
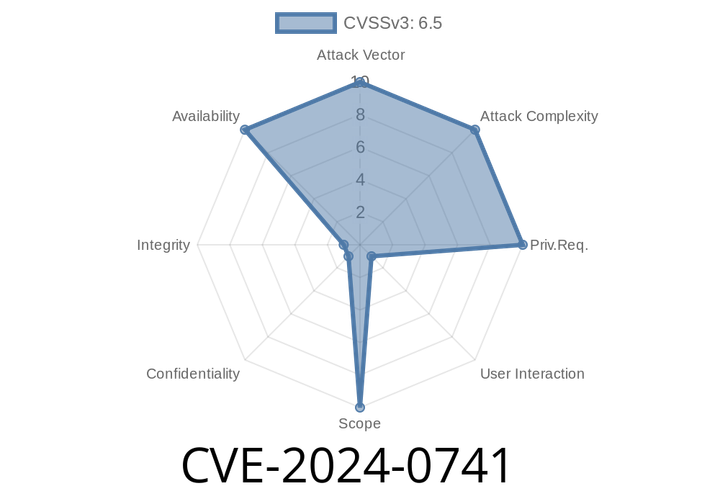
CVE-2024-0741 - How an Out-of-Bounds Write in ANGLE Exposed Firefox & Thunderbird to Exploitable Crashes
---
In the fast-moving world of web browsers, security flaws can lead to big problems. Let's talk about CVE-2024-0741, a real
Episode
00:00:00
00:00:00