CVE-2023-47248 - Exploiting PyArrow’s Dangerous Deserialization – What Developers Must Know
In November 2023, a major security vulnerability was disclosed for PyArrow, identified as CVE-2023-47248. This flaw lurks in the way PyArrow handles deserializing
CVE-2023-5996 - Inside the “Use-After-Free” Exploit in Google Chrome’s WebAudio Engine (Full Technical Breakdown)
In November 2023, Google patched a critical security vulnerability in Chrome’s WebAudio component: CVE-2023-5996. This high-severity flaw could let an attacker
CVE-2023-38547 - How Attackers Can Use Veeam ONE’s SQL Server Info Leak for RCE
Veeam ONE is a popular monitoring and reporting solution for backup infrastructures—used worldwide by many companies. But in June 2023, a serious security hole,
CVE-2023-45827 - How a Prototype Pollution Bug in Dot Diver Could Lead to Remote Code Execution
Dot diver is a TypeScript utility library that makes it easy to work with object paths written in dot notation. It's lightweight, dependency-
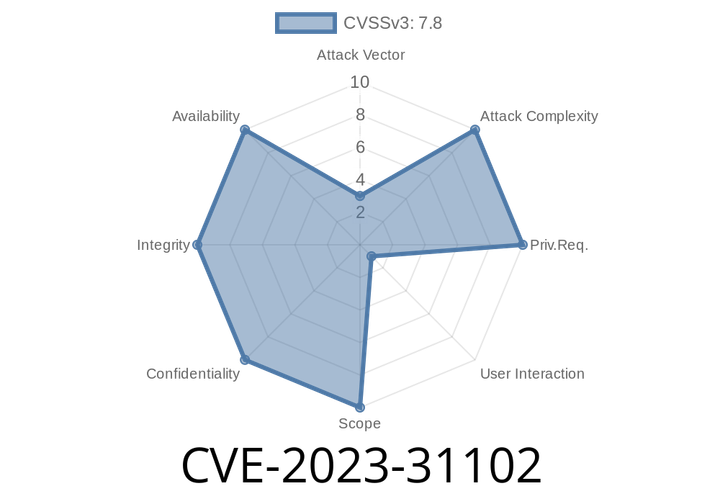
CVE-2023-31102 - How a Sneaky Bug in 7-Zip’s Ppmd7.c Opened the Door to Security Risks
When it comes to compressing and decompressing files on Windows, few tools are as widely used as 7-Zip. Reliable, open-source, free—it’s
Episode
00:00:00
00:00:00