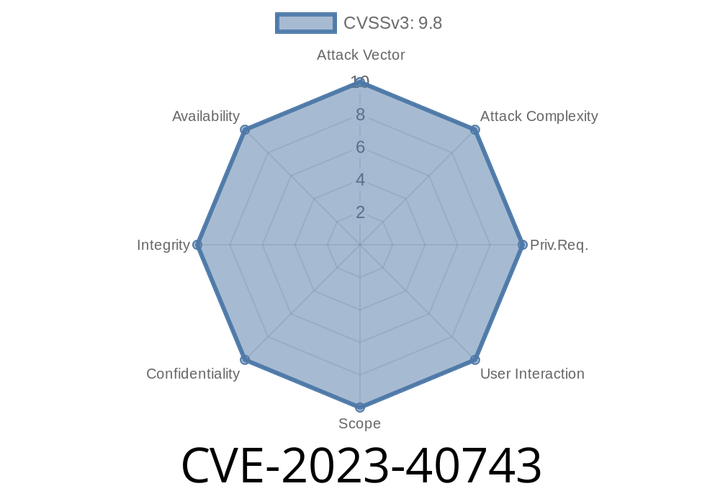
CVE-2023-40743 - Dangerous Service Lookups in Apache Axis 1.x Can Lead to RCE, SSRF, and DOS
In August 2023, a high-impact vulnerability was disclosed affecting applications based on Apache Axis 1.x, a Java-based SOAP engine. Identified as CVE-
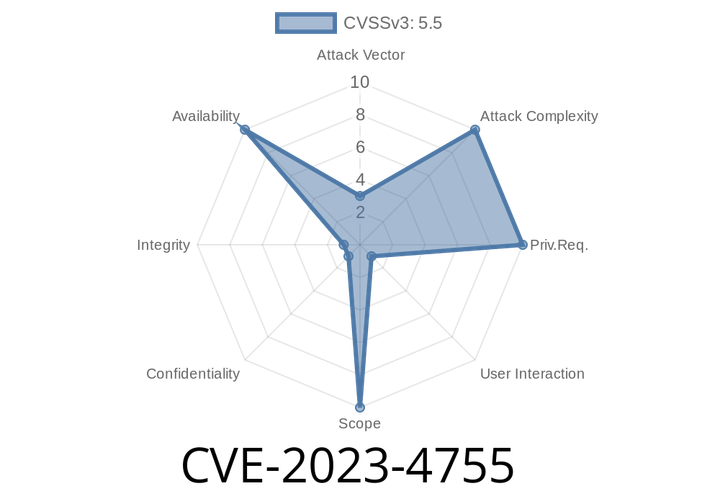
CVE-2023-4755 - How the Use-After-Free Bug in gpac/gpac <2.3-DEV Was Found and Exploited
In September 2023, a critical software bug was discovered in the popular open-source multimedia framework, gpac/gpac. Labeled CVE-2023-4755, this vulnerability is
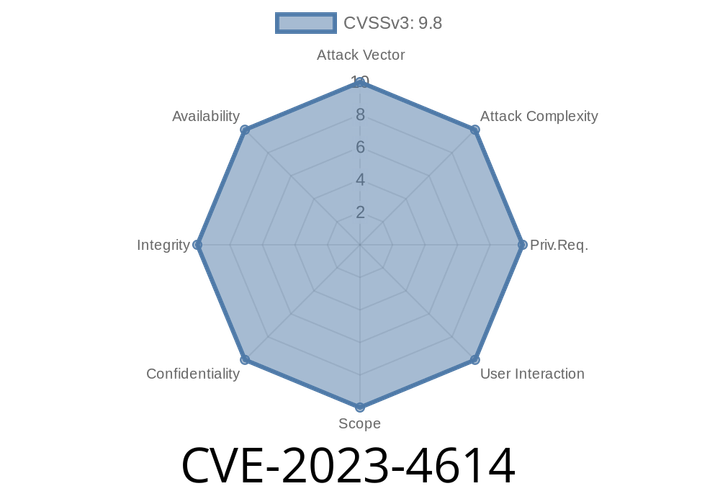
CVE-2023-4614 - How Remote Attackers Can Take Over LG LED Assistant via setThumbnailRc Endpoint
---
LG’s LED Assistant is a tool used to control and customize large screen displays, especially in commercial environments. In mid-2023, a critical vulnerability
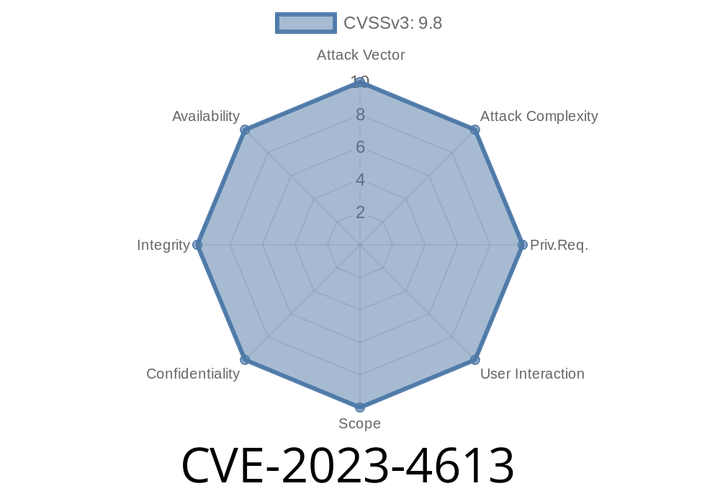
CVE-2023-4613 - LG LED Assistant Remote Code Execution Exploit Explained
In June 2023, a critical security flaw was revealed in LG LED Assistant, making it possible for attackers on the Internet to run any code
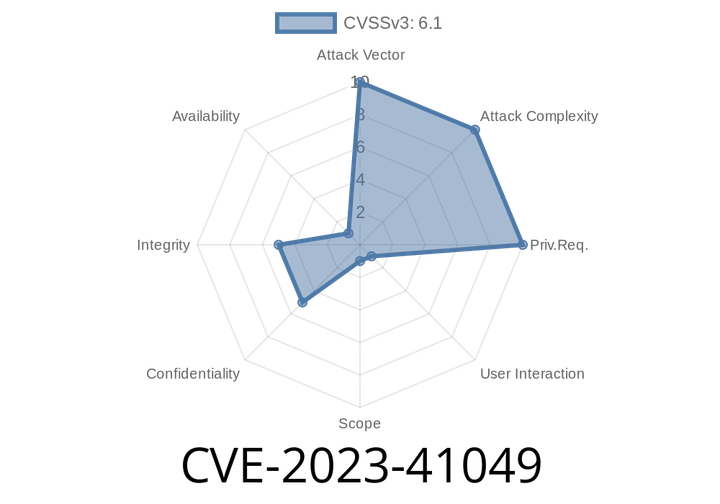
CVE-2023-41049 - Critical Remote Code Execution in @dcl/single-sign-on-client npm Library — What It Is and How to Stay Safe
If you’re building web applications with Node.js, you may be familiar with npm libraries that simplify authentication, like @dcl/single-sign-on-client.
Episode
00:00:00
00:00:00