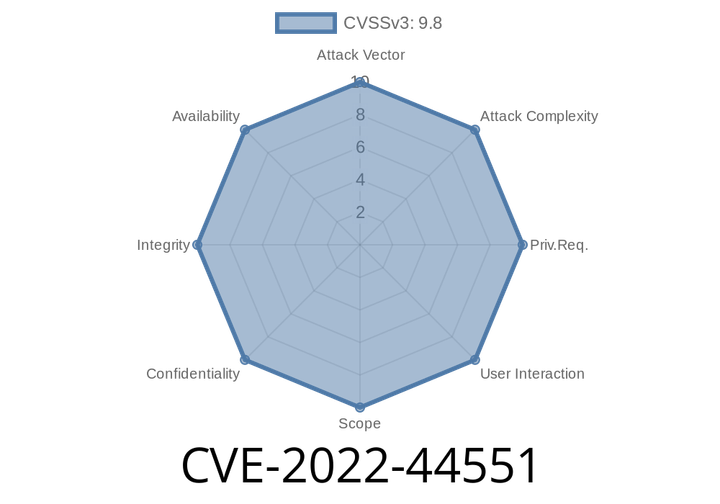
CVE-2022-44551 The iaware module has a vulnerability in thread security
This issue results because thread_id in the password settings is not verified before being used. This can result in an attacker gaining root privileges.
CVE-2022-3446 - Heap Buffer Overflow in WebSQL – What Happened, How It Works, and How Attackers Could Exploit It
On October 2022, security researchers revealed CVE-2022-3446, a serious flaw affecting Google Chrome's WebSQL implementation. WebSQL is an old database feature
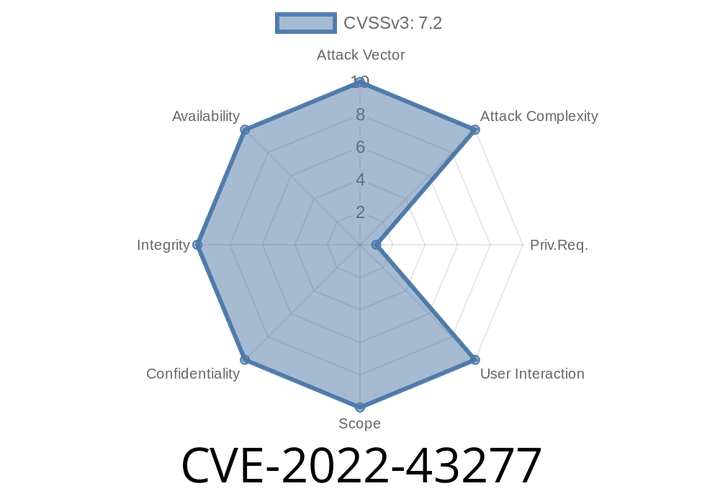
CVE-2022-43277 Canteen Management System v1.0 had an arbitrary file upload vulnerability.
Attackers can upload a PHP script to execute code on the server. The file upload feature is enabled by default in Canteen. Note that this
CVE-2022-40797 - How a Simple Upload Bypass in Roxy Fileman 1.4.6 Leads to Remote Code Execution (.phar Upload Exploit)
If you use Roxy Fileman 1.4.6—an open-source web file manager popular among PHP developers for WYSIWYG editors like TinyMCE and CKEditor—
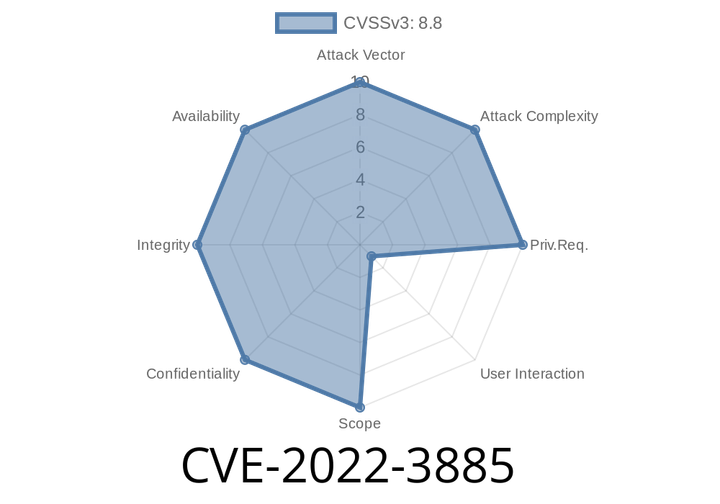
CVE-2022-3885 - Exploiting Use-After-Free in V8 JavaScript Engine of Chrome – Detailed Guide
---
Introduction
In 2022, a critical vulnerability was found in the V8 JavaScript engine, which powers Google Chrome and other Chromium-based browsers (like Edge and
Episode
00:00:00
00:00:00