CVE-2022-40742 - Local File Inclusion in Mail SQR Expert System — How It Works & Example Exploits
Mail SQR Expert is a web-based management system mainly used for mail and ticketing solutions in organizations. In late 2022, a critical vulnerability was
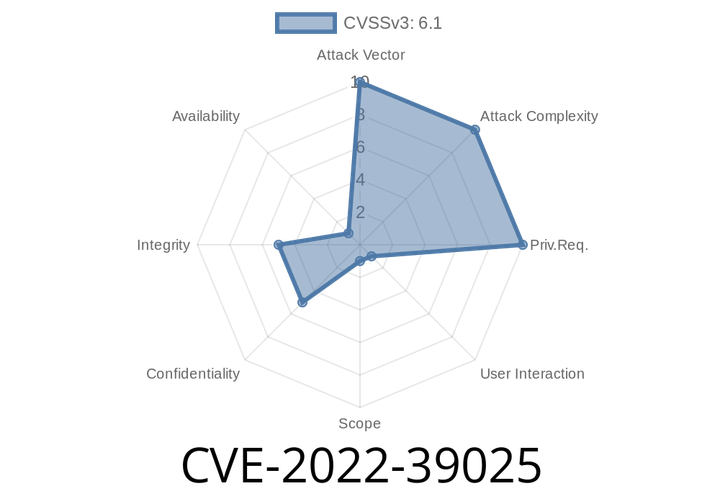
CVE-2022-39025 U-Office Force PrintMessage function has insufficient filtering for special characters
To do that, he/she has to send malicious URL with special characters to a user who has enabled this Force Print feature in the
CVE-2022-44019 - Remote Command Execution in Total.js 4 `/api/common/ping` Endpoint
In November 2022, a critical vulnerability was found in the Total.js 4 framework, before commit e5ace7. This security bug, now known as CVE-2022-
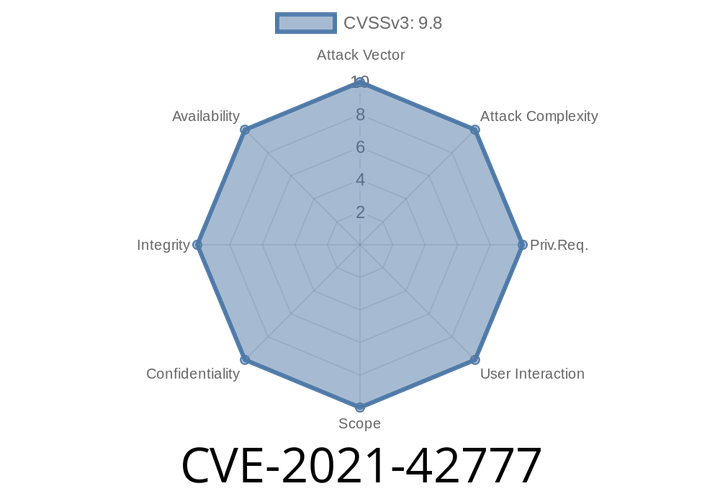
CVE-2021-42777 - RCE via Stimulsoft Reports – Exploiting Insecure Compilation Mode
Stimulsoft Reports is a widely used reporting tool for .NET, often embedded in enterprise web and desktop applications. But if you’re still running version
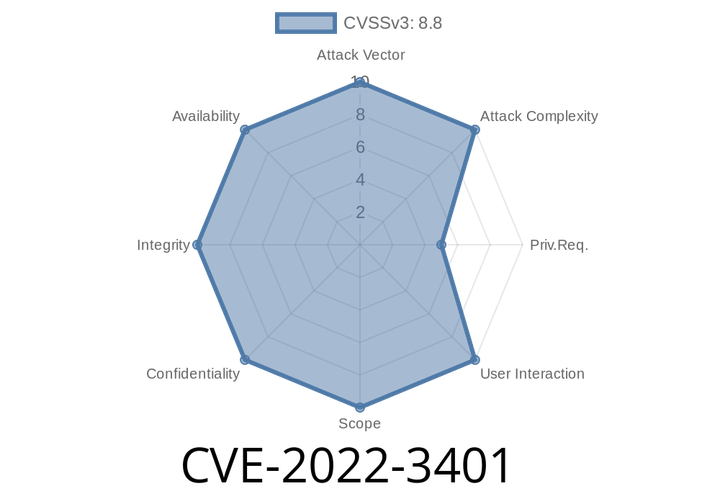
CVE-2022-3401 - Remote Code Execution in Bricks WordPress Theme (Versions 1.2 – 1.5.3)
WordPress powers more than 40% of all websites, and its extensibility through themes and plugins is both a strength and a weakness. In mid-2022,
Episode
00:00:00
00:00:00