CVE-2022-43228 - SQL Injection Vulnerability in Barangay Management System v1. (Detailed Analysis & Exploitation)
Barangay Management System v1. is a web application used by local municipalities in some countries to manage citizen records, issue clearances, and handle administrative tasks.
CVE-2021-38734 - How an SQL Injection in SEMCMS SHOP v1.1’s Ant_Menu.php Opens the Door for Attackers
---
SEMCMS SHOP is a popular e-commerce CMS solution, especially in certain markets needing a light and manageable online store. In September 2021, a dangerous
CVE-2021-38736 SEMCMS Shop V 1.1 is vulnerable to SQL Injection via Ant_Global.php.
It is recommended to use a different password for the administrator account.
SEMCMS Shop V 1.1 is vulnerable to Cross-site Scripting via Settings.
CVE-2022-43275 - Exploiting Arbitrary File Upload in Canteen Management System v1.
---
CVE-ID: CVE-2022-43275
Vulnerability Type: Arbitrary File Upload
Affected Product: Canteen Management System v1.
Component: /youthappam/php_action/editProductImage.php
Impact: Remote Code
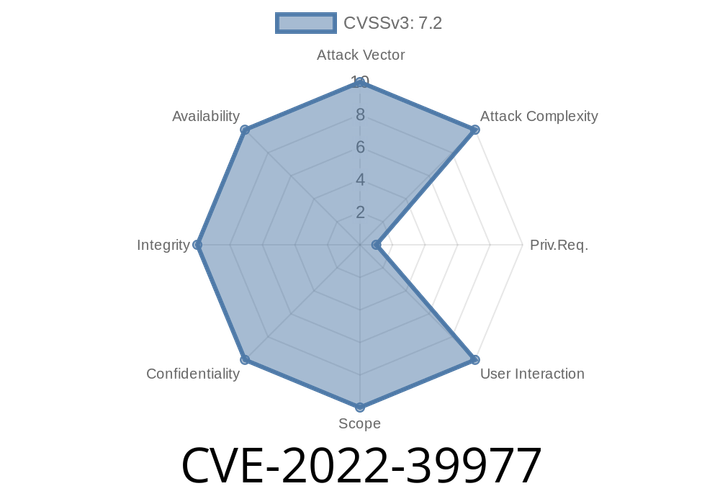
CVE-2022-39977 - How Attackers Exploit the Arbitrary File Upload in Online Pet Shop Web App v1.
In 2022, security researchers discovered a critical vulnerability in the Online Pet Shop Web App v1.. Tracked as CVE-2022-39977, this flaw allows attackers
Episode
00:00:00
00:00:00