CVE-2022-41537 The v1.0 of the Tours & Travels Management System had an arbitrary file upload vulnerability.
This issue is rated as critical due to the fact that it could be exploited by hackers to carry out a massive data breach. Furthermore,
CVE-2022-41504 An upload vulnerability in the component /php_action/editProductImage.php of Billing System Project v1.0 allows attackers to execute arbitrary code.
In addition, there are other cross site request forgery, SQL injection, and file upload issues. The following are the high level details of the arbitrary
CVE-2022-3584 A critical vulnerability was found in SourceCodester Canteen Management System 1.0. The id argument can be manipulated for sql injection.
This software can be exploited via Remote Code Execution and RCE. Some file extensions may be affected. These are edituser.php, editgroup.php, editgroup2.php,
CVE-2022-42142 Ip/tour/admin/operations/update_settings.php is vulnerable to arbitrary code execution.
An attacker can inject malicious code into update_settings.php to execute any malicious code on the system. An attacker can also inject malicious code
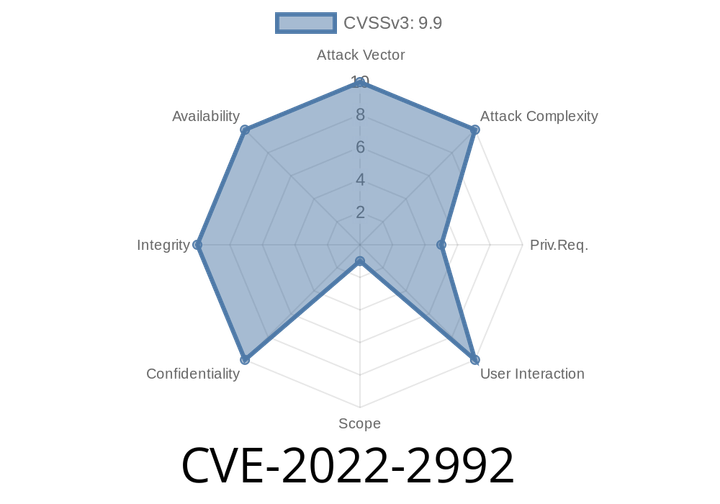
CVE-2022-2992 - How a GitLab Bug Let Attackers Run Code Through the GitHub Import API
In June 2022, a dangerous vulnerability—CVE-2022-2992—was discovered in GitLab CE/EE. This issue affected all versions from 11.10 up to
Episode
00:00:00
00:00:00