CVE-2022-42154 - How Arbitrary File Upload in 74cmsSE v3.13. Can Lead to Remote Code Execution
Security vulnerabilities in web applications are a constant threat. One particularly dangerous bug is an arbitrary file upload vulnerability, which often leads to Remote Code
CVE-2022-41472 An XSS vulnerability was found in CMS v3.12.0 via the apiadmin/notice/add component.
The XSS flaw can be exploited by remote attackers via a request to the component /apiadmin/notice/add. An attacker can inject script codes in
CVE-2022-42171 Tenda AC10 V15.03.06.23 contains a Stack overflow vulnerability via /goform/saveParentControlInfo.
Tenda AC10 V15.03.06.23 has a Cross-site scripting(XSS) vulnerability via /goform/saveParentControlInfo.
Tenda AC10 V15.03.06.23 has a SQL
CVE-2022-3549 An issue was found in SourceCodester Simple Cold Storage Management System 1.0 that affects Avatar Handler file processing.
This vulnerability is related to the one found in a different CMS software. It is advised to apply the solution provided in the linked advisory.
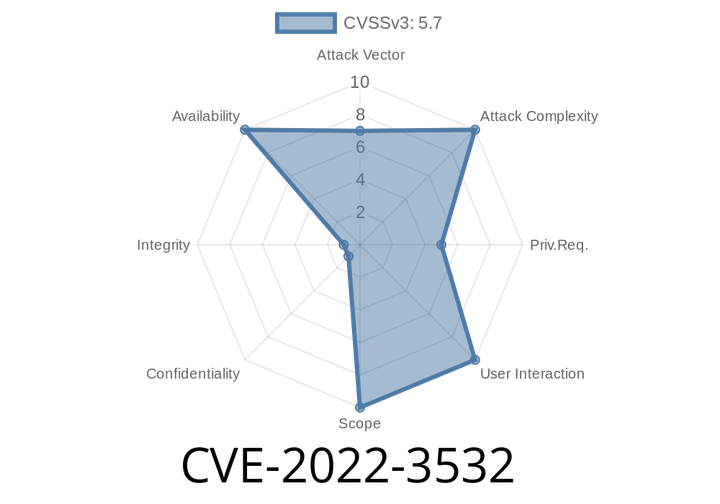
CVE-2022-3532 Vulnerability found in BPF component. It has memory leak.
It has been found that when BPF component is enabled, it results in memory leaks. These memory leaks might be exploited by the attackers. The
Episode
00:00:00
00:00:00