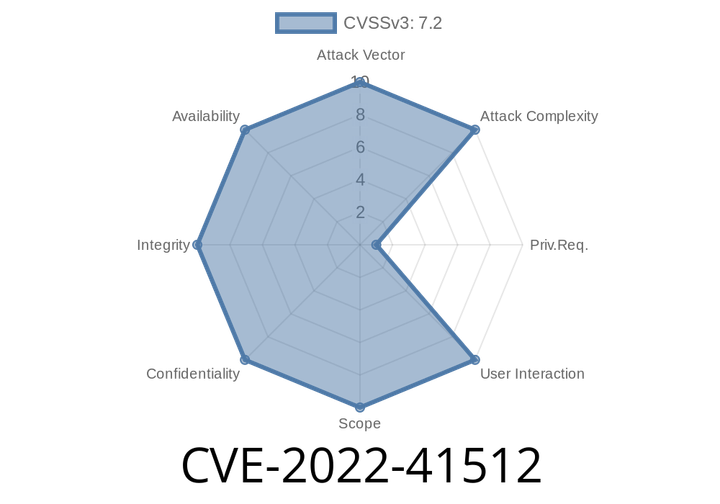
CVE-2022-41512 An arbitrary file upload vulnerability in the /php_action/editFile.php of Online Diagnostic Lab Management System v1.0 allows attackers to execute arbitrary code.
The component /php_action/editFile.php does not require any authentication to enable unauthorized users to upload files and execute code. The component should be
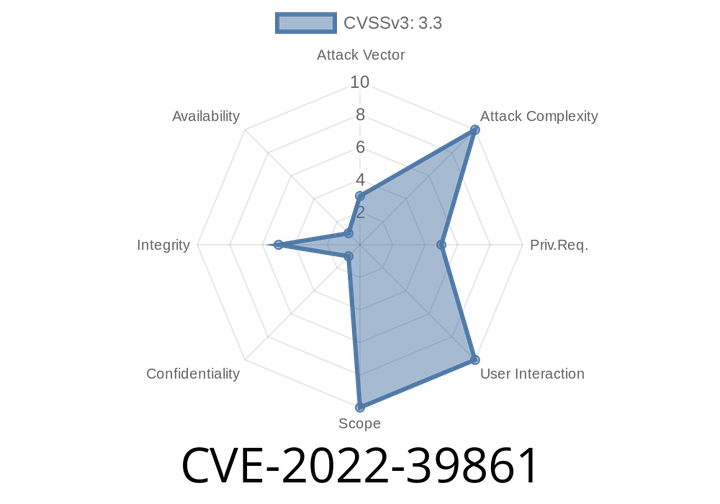
CVE-2022-39861 Camera before 3.5.51 has an unprotected receiver that can be recorded by attackers.
When using the Camera API with Android 4.4, avoid using the Camera2 API as it has a high risk of being exploited via a
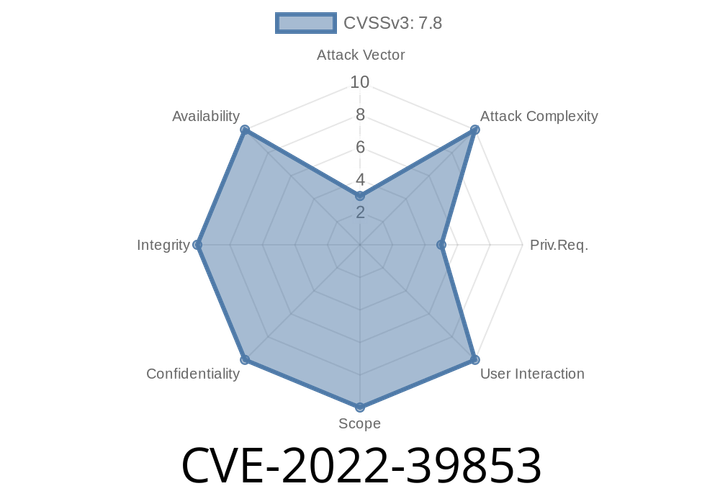
CVE-2022-39853 The perf-mgr driver has a use after free vulnerability. An attacker can cause a memory access fault.
Attacker can use this flaw to execute code in user mode with kernel privileges. This issue can be exploited by an attacker when user open
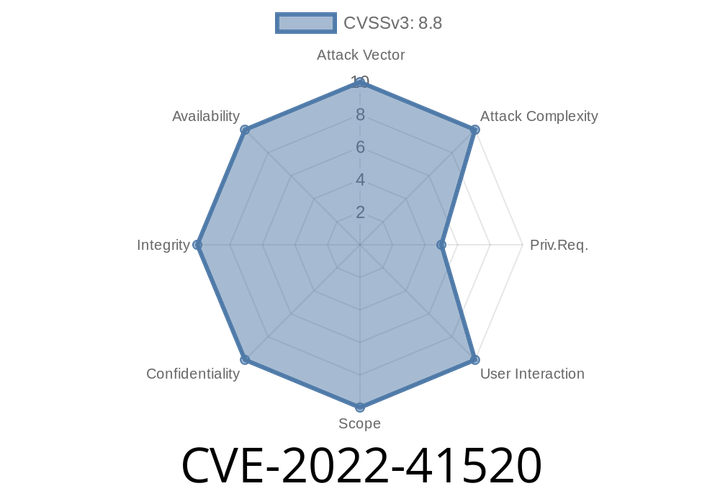
CVE-2022-41520 - Exploiting an Authenticated Stack Overflow in TOTOLINK NR180X (UploadCustomModule File Parameter)
In late 2022, researchers uncovered a serious vulnerability—CVE-2022-41520—in the TOTOLINK NR180X router, firmware version V9.1.u.6279_B20210910. This flaw
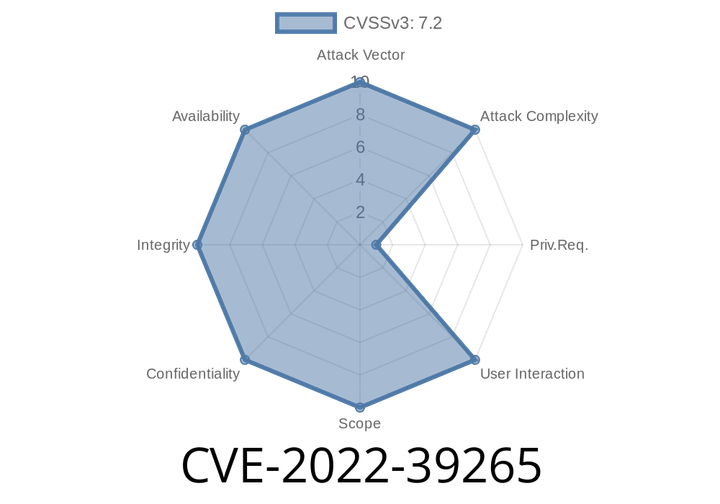
CVE-2022-39265 MyBB is a free and open source forum software
It is enabled by default and likely did not have any additional configuration steps taken. If a MyBB installation was upgraded to a vulnerable MyBB
Episode
00:00:00
00:00:00