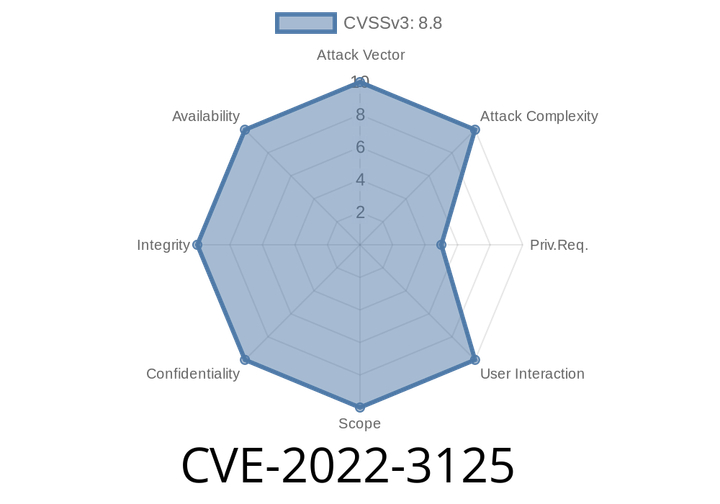
CVE-2022-3125 The Frontend File Manager Plugin before 21.3 allows any authenticated user to rename a file to an arbitrary extension, such as PHP, and upload arbitrary files on the server.
this can be very dangerous for a variety of reasons. One example is that the plugin does not have security features in place to prevent
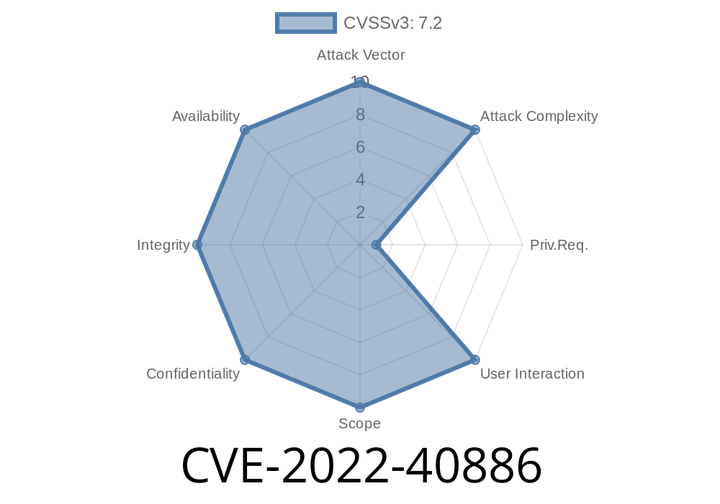
CVE-2022-40886 DedeCMS 5.7.98 has a file upload vulnerability in the background.
In rare cases, the uploaded file can be executed remotely. This is possible due to the nature of PHP, which executes script code. This vulnerability
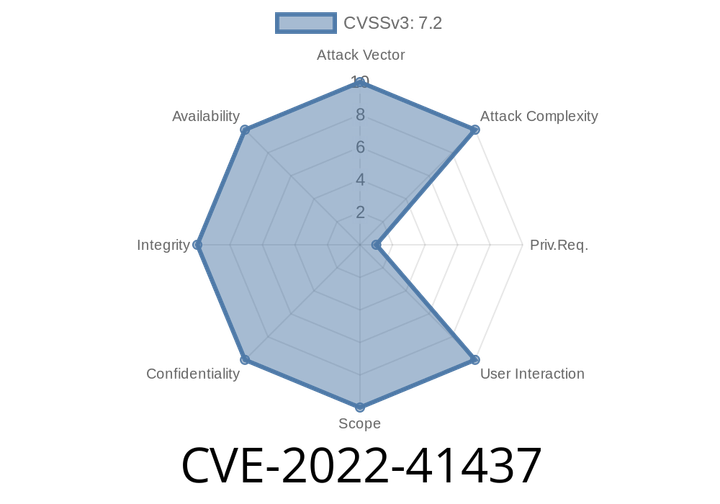
CVE-2022-41437 Billing System Project v1.0 had a remote code execution vulnerability in the createProduct.php component.
This can be leveraged to install a custom PHP script onto the system via a remote attacker. An attacker can leverage this RCE vulnerability to
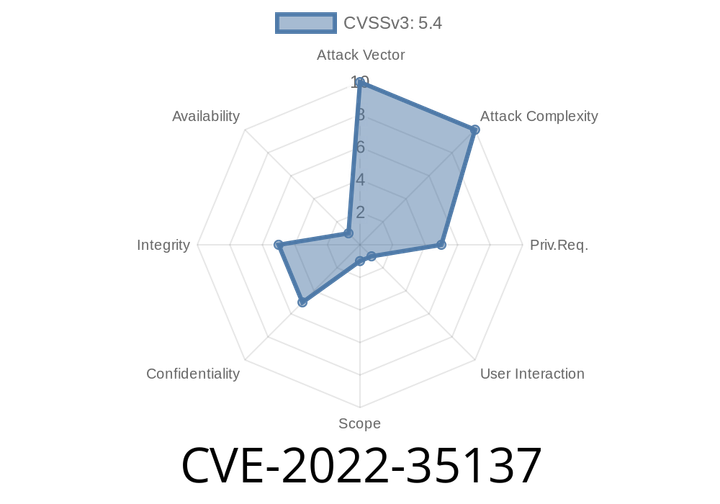
CVE-2022-35137 DGIOT 4.5.4 had multiple XSS vulnerabilities.
These issues could be exploited by malicious people to conduct cross-site scripting attacks. A total of 14 XSS flaws were found in DGIOT Lightweight
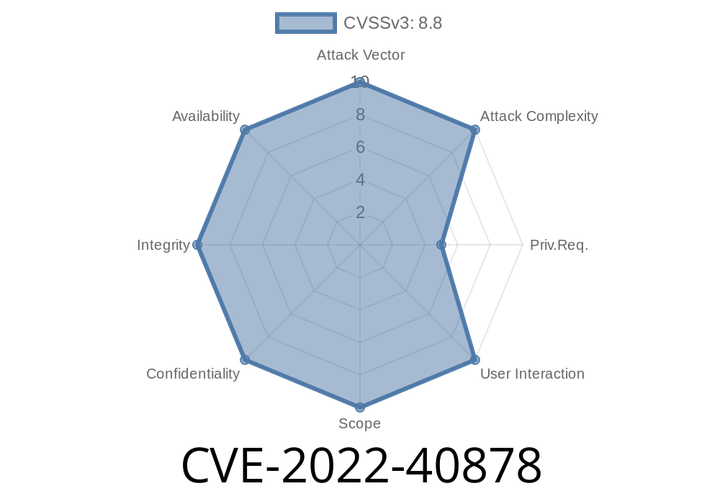
CVE-2022-40878 Exam Reviewer Management System 1.0 allows an attacker to upload a web-shell php file and achieve RCE.
An attacker can do this by setting up a fake facebook account or by manipulating the system to access the system’s data. By uploading
Episode
00:00:00
00:00:00