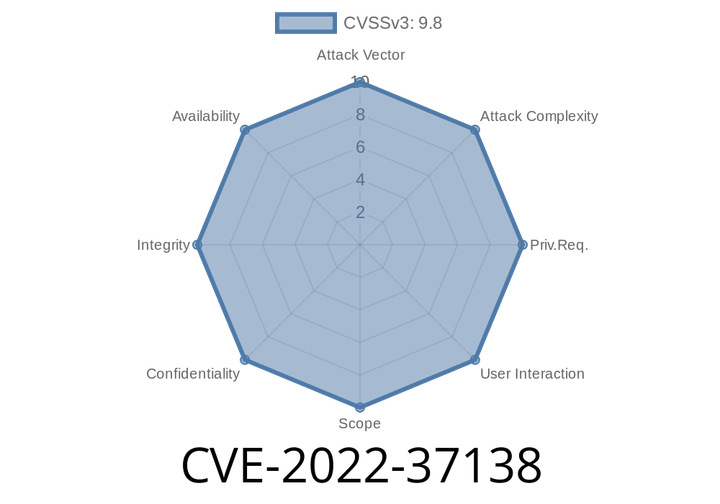
CVE-2022-37138 The LMS 1.0 is vulnerable to SQL Injection at the login page, which allows attackers to log in as Administrator as username form.
To inject SQL Injection, attacker can send request with SQL statement in the ‘INPUT>’ tag. An attacker can send the following injection request to
CVE-2022-35805 - Breaking Down the Microsoft Dynamics CRM Remote Code Execution Flaw
---
In the world of business software, Microsoft Dynamics CRM (on-premises) powers customer relations for thousands of organizations. But in 2022, a major security risk
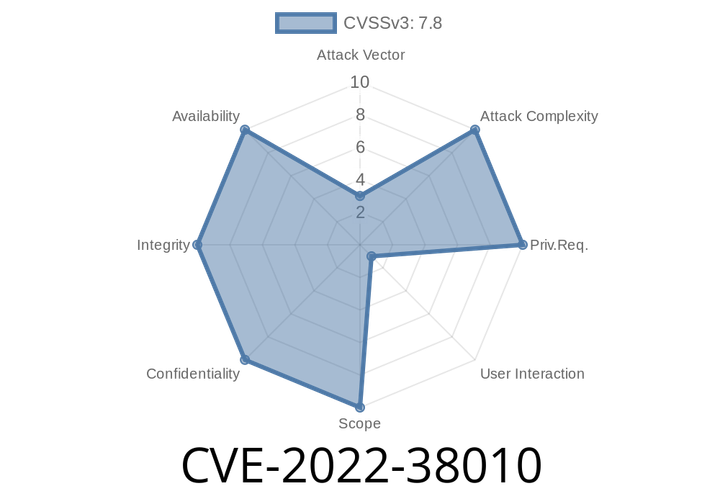
CVE-2022-38010 Microsoft Office Visio Remote Code Execution Vulnerability
This vulnerability is within the OLE ActiveX control, and can be exploited by a remote attacker via the Microsoft Office application. To exploit this vulnerability,
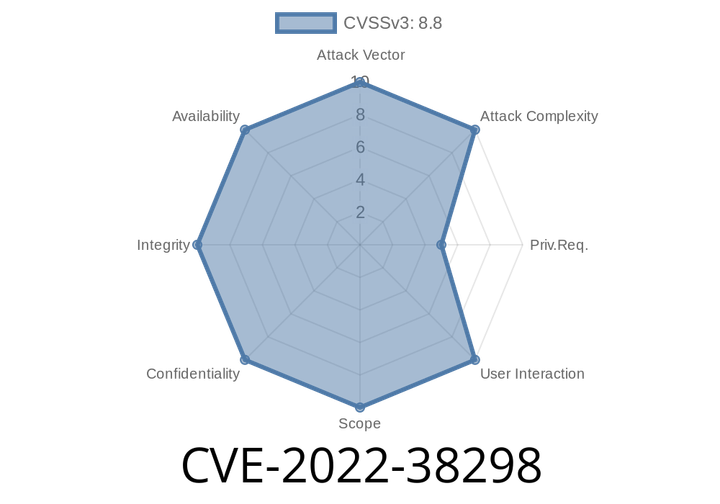
CVE-2022-38298 AppSmith v1.7.11 allowed attackers to execute SSRF via the AWS internal metadata endpoint.
This vulnerability allows an attacker to control and manipulate the AWS internal configuration settings by sending a SSRF request to the AWS internal metadata endpoint.
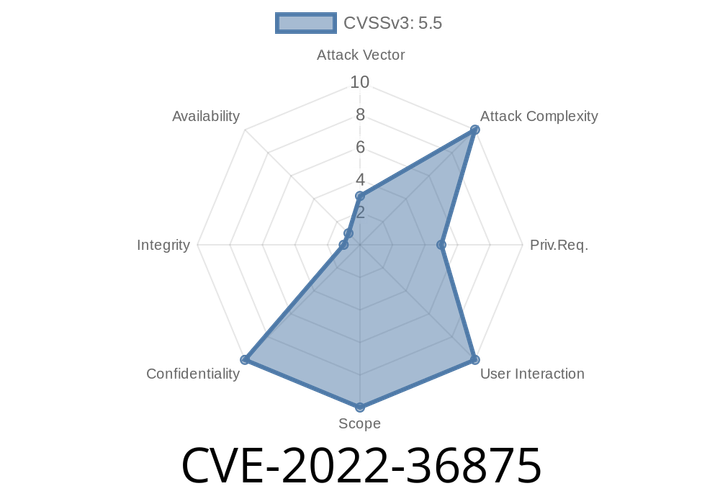
CVE-2022-36875 The Water plugin prior to version 2.2.11.22081151 allows an attacker to access the file without permission.
There is a programming error that allows to access the file on device without permission.
In order to exploit this issue, an attacker has to
Episode
00:00:00
00:00:00