
CVE-2022-24487 - Breaking Down the Windows LSA Remote Code Execution Vulnerability
The Microsoft Windows Local Security Authority (LSA) is a key part of any Windows device’s security. It handles sensitive operations like user logon, token

CVE-2022-26812 - How Hackers Could Have Taken Over Windows DNS Servers (Explained)
When it comes to Windows Server security, DNS has always been a prime target. In 2022, a particularly dangerous flaw was found in Microsoft’s
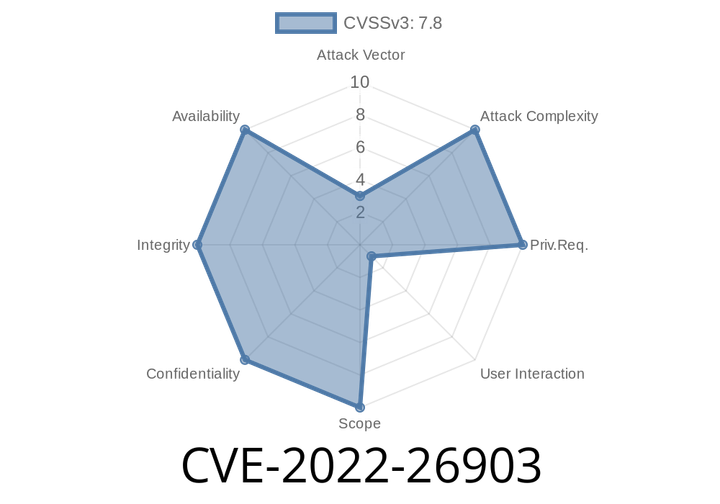
CVE-2022-26903 Windows Graphics Component Remote Code Execution Vulnerability.
The vulnerability is due to a stack buffer overflow in LibXcomps, which can be exploited by malicious attackers to execute arbitrary code on the affected

CVE-2022-24818 - Critical JNDI Vulnerability in GeoTools Library—Explained
GeoTools is a widely-used open source Java library for handling geospatial (map/geography) data. By providing an extensive toolkit for reading, manipulation, and writing

CVE-2022-22958 - Remote Code Execution in VMware Workspace ONE Access—How Attackers Exploit Deserialization in JDBC URIs
Earlier this year, VMware announced two dangerous vulnerabilities (CVE-2022-22957 & CVE-2022-22958) in some of their most widely used products: Workspace ONE
Episode
00:00:00
00:00:00